從Google Drive中免費下載最新的VCESoft HPE7-A02 PDF版考試題庫:https://drive.google.com/open?id=1sEBrTntZQd1uVPXyIyJhnEzCvIWxU1GN
VCESoft是一個為HP人士參加相關認證考試提供資源的便利網站。VCESoft針對不同的考生有不同的培訓方法和不同的培訓課程。有了VCESoft提供的這些針對性的培訓,考生通過HPE7-A02相關考試就容易得多。很多曾經參加HPE7-A02專業相關認證考試的人都是通過我們的VCESoft提供的測試練習題和答案考過的,因此VCESoft在HP行業中得到了很高的聲譽。
HPE7-A02認證計劃在全球得到認可,在IT行業受到高度重視。該認證計劃旨在幫助IT專業人員提高其網絡安全技能和知識,以幫助他們獲得更好的工作機會和更高的薪水。對於正在尋找合格且技能精湛的網絡安全專業人員來保護其網絡免受網絡攻擊的組織來說,該認證計劃也有益。
如果你參加HP HPE7-A02認證考試,你選擇VCESoft就是選擇成功!祝你好運。
為了準備HPE7-A02考試,考生可以利用各種資源,包括培訓課程、教材指南、練習考試和使用Aruba技術的實踐經驗。成功的考生將能夠展示他們對網絡安全概念的了解和將該知識應用於使用Aruba解決方案保護無線網絡的能力。ACNSP認證可以幫助IT專業人員推進他們的職業生涯,向潛在雇主展示他們的專業知識。
考試涵蓋了與網絡安全相關的廣泛主題,包括無線安全協議、訪問控制、身份驗證和加密、網絡設計和實施以及威脅檢測和緩解。它還涵蓋了高級主題,例如網絡取證、合規性法規和網絡安全最佳實踐。
問題 #72
A company issues user certificates to domain computers using its Windows CA and the default user certificate template. You have set up HPE Aruba Networking ClearPass Policy Manager (CPPM) to authenticate 802.1X clients with those certificates. However, during tests, you receive an error that authorization has failed because the usernames do not exist in the authentication source.
What is one way to fix this issue and enable clients to successfully authenticate with certificates?
答案:C
解題說明:
To fix the issue where authorization fails because the usernames do not exist in the authentication source, you can configure rules in HPE Aruba Networking ClearPass Policy Manager (CPPM) to strip the domain name from the username. When certificates are issued by a Windows CA, the username in the certificate often includes the domain (e.g., user@domain.com). ClearPass might not be able to find this format in the authentication source. By stripping the domain name, you ensure that ClearPass searches for just the username (e.g., user) in the authentication source, allowing successful authentication.
問題 #73
You have enabled "rogue AP containment" in the Wireless IPS settings for a company's HPE Aruba Networking APs. What form of containment does HPE Aruba Networking recommend?
答案:A
解題說明:
* Rogue AP Containment Methods:
* HPE Aruba Networking recommends using wireless deauthentication as the preferred method for rogue AP containment.
* Deauthentication sends deauth frames to clients connected to rogue APs, causing them to disconnect. This method is effective without introducing unnecessary disruptions to the wired infrastructure.
* Key Points:
* Wireless Deauthentication is simple, efficient, and widely supported across client devices.
* Tarpit Containment is more aggressive and may cause unintentional disruptions to legitimate clients.
* Wired Containment involves blocking traffic at the switch level but is complex and may impact legitimate infrastructure traffic.
* Option Analysis:
* Option A: Correct. Wireless deauthentication is the recommended method as it targets rogue AP clients without excessive network impact.
* Option B: Incorrect. Combining wireless tarpit and wired containment is overkill and not typically recommended.
* Option C: Incorrect. Wireless tarpit can be effective but is generally not the first choice due to its aggressive nature.
* Option D: Incorrect. Wired containment is more complex and reserved for specific use cases, not general recommendations.
問題 #74
A company is implementing HPE Aruba Networking Wireless IDS/IPS (WIDS/WIPS) on its AOS-10 APs, which are managed in HPE Aruba Networking Central.
What is one requirement for enabling detection of rogue APs?
答案:D
解題說明:
To enable the detection of rogue APs with HPE Aruba Networking Wireless IDS/IPS (WIDS/WIPS) on AOS-10 APs managed in HPE Aruba Networking Central, each AP must have a Foundation with Security license. This license enables advanced security features, including rogue AP detection, which is crucial for maintaining a secure wireless environment and protecting against unauthorized access points.
問題 #75 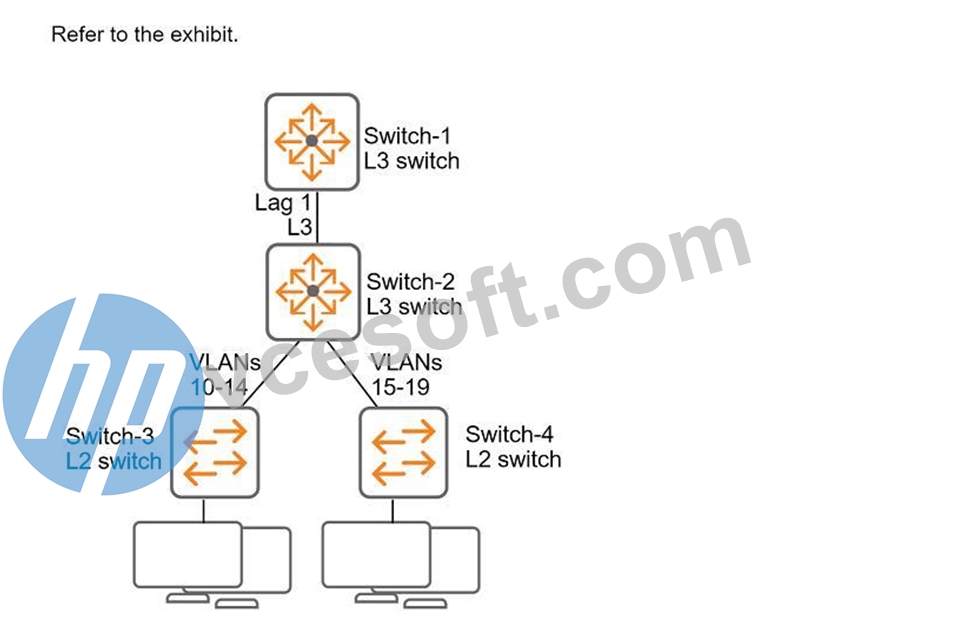
All of the switches in the exhibit are AOS-CX switches.
What is the preferred configuration on Switch-2 for preventing rogue OSPF routers in this network?
答案:A
解題說明:
To prevent rogue OSPF routers in the network shown in the exhibit, the preferred configuration on Switch-2 is to configure OSPF authentication on Lag 1 in MD5 mode. This setup enhances security by ensuring that only routers with the correct MD5 authentication credentials can participate in the OSPF routing process.
This method protects the OSPF sessions against unauthorized devices that might attempt to introduce rogue routing information into the network.
1.OSPF Authentication: Implementing MD5 authentication on Lag 1 ensures that OSPF updates are secured with a cryptographic hash. This prevents unauthorized OSPF routers from establishing peering sessions and injecting potentially malicious routing information.
2.Secure Communication: MD5 authentication provides a higher level of security compared to simple password authentication, as it uses a more robust hashing algorithm.
3.Applicability: Lag 1 is the primary link between Switch-1 and Switch-2, and securing this link helps protect the integrity of the OSPF routing domain.
問題 #76
A company is implementing a client-to-site VPN based on tunnel-mode IPsec.
Which devices are responsible for the IPsec encapsulation?
答案:C
解題說明:
In a client-to-site VPN based on tunnel-mode IPsec, the remote clients and a gateway at the main site are responsible for the IPsec encapsulation. The remote clients initiate the VPN connection and encapsulate their traffic in IPsec, which is then decapsulated by the gateway at the main site.
1.IPsec Encapsulation: The remote clients encapsulate their traffic using IPsec protocols before sending it over the internet to the main site.
2.Gateway Role: The gateway at the main site receives the encapsulated traffic, decapsulates it, and forwards it to the internal network. Similarly, traffic from the main site to the remote clients is encapsulated by the gateway and decapsulated by the clients.
3.Security: This setup ensures that data is securely transmitted between the remote clients and the main site, protecting it from eavesdropping and tampering.
問題 #77
......
HPE7-A02熱門題庫: https://www.vcesoft.com/HPE7-A02-pdf.html
P.S. VCESoft在Google Drive上分享了免費的2025 HP HPE7-A02考試題庫:https://drive.google.com/open?id=1sEBrTntZQd1uVPXyIyJhnEzCvIWxU1GN
