Our Cisco Exam Questions greatly help Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) exam candidates in their preparation. Our Cisco 300-215 practice questions are designed and verified by prominent and qualified Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) exam dumps preparation experts. The qualified Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) exam questions preparation experts strive hard and put all their expertise to ensure the top standard and relevancy of 300-215 exam dumps topics.
Cisco 300-215 exam is a certification exam conducted by Cisco. 300-215 exam is designed to test the knowledge and skills of cybersecurity professionals in conducting forensic analysis and incident response using Cisco technologies. 300-215 exam is one of the most sought-after certifications in the cybersecurity industry, and it validates the candidate's expertise in cybersecurity incident response and forensic analysis.
Cisco 300-215 exam is an essential certification for those who aspire to work in the field of cybersecurity. 300-215 Exam focuses on the practical aspects of conducting forensic analysis and incident response using Cisco Technologies. It tests the candidates' ability to handle real-world cybersecurity scenarios and provides a career path for cybersecurity professionals. Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps certification is highly valued by employers and is an industry-recognized standard for incident response and forensic analysis.
There are a lot of advantages of our APP online version. On one hand, the online version of our 300-215 exam questions can apply in all kinds of the eletronic devices. In addition, the online version of our 300-215 training materials can work in an offline state. If you buy our products, you have the chance to use our study materials for preparing your exam when you are in an offline state. We believe that you will like the online version of our 300-215 Exam Questions.
The following will be discussed in CISCO 300-215 Exam Dumps:
NEW QUESTION # 106
A new zero-day vulnerability is discovered in the web application. Vulnerability does not require physical access and can be exploited remotely. Attackers are exploiting the new vulnerability by submitting a form with malicious content that grants them access to the server. After exploitation, attackers delete the log files to hide traces. Which two actions should the security engineer take next? (Choose two.)
Answer: B,D
Explanation:
* Input validation (A) is a critical countermeasure to defend against command injection and related vulnerabilities, as discussed in the Cisco guide. Proper validation ensures that malicious commands or payloads are not accepted or executed by the web application.
* File integrity monitoring (E) helps detect unauthorized changes such as log deletion or binary modification, making it a crucial tool in recognizing and investigating tampering attempts.Blocking port
443 (B) would disable HTTPS and is not a practical solution. Antivirus (C) does not prevent form- based application attacks, and merely updating the application (D) may not be sufficient without addressing the underlying input validation flaw.
-
NEW QUESTION # 107
An incident response team is recommending changes after analyzing a recent compromise in which:
a large number of events and logs were involved;
team members were not able to identify the anomalous behavior and escalate it in a timely manner; several network systems were affected as a result of the latency in detection; security engineers were able to mitigate the threat and bring systems back to a stable state; and the issue reoccurred shortly after and systems became unstable again because the correct information was not gathered during the initial identification phase.
Which two recommendations should be made for improving the incident response process? (Choose two.)
Answer: B,D
NEW QUESTION # 108 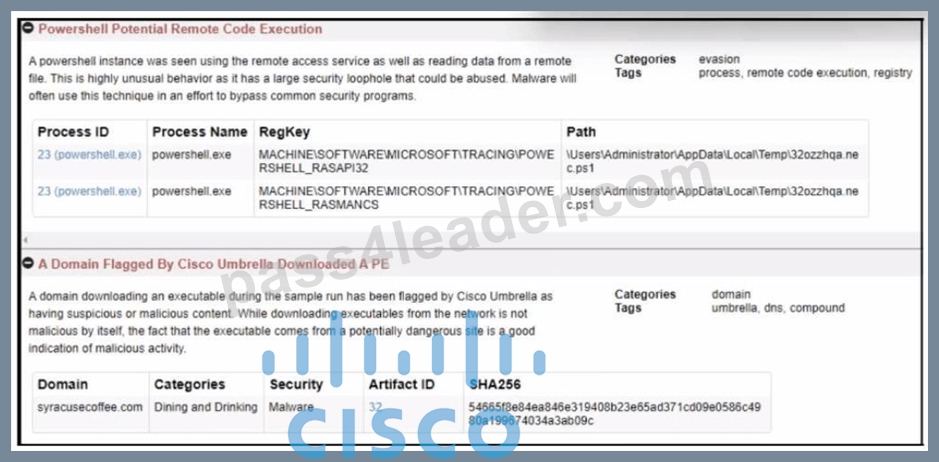
Answer: B
Explanation:
The correct next step in analyzing the malicious nature of the email is toevaluate the artifactsinCisco Secure Malware Analytics(formerly Threat Grid). This tool provides a comprehensive sandbox environment where behavioral indicators like file execution, registry access, and domain connections are logged and scored.
The exhibit shows:
* Remote PowerShell execution
* Executable download from a flagged domain
* SHA256 hash linked to malware
All these artifacts, as labeled in the Secure Malware Analytics output, arekey indicators of compromise, and analyzing them further can confirm whether the email was part of a malicious campaign.
Thus, the best action is:
A). Evaluate the artifacts in Cisco Secure Malware Analytics.
NEW QUESTION # 109
What is the steganography anti-forensics technique?
Answer: C
Explanation:
Reference:
https://blog.eccouncil.org/6-anti-forensic-techniques-that-every-cyber-investigator-dreads/
NEW QUESTION # 110
Refer to the exhibit.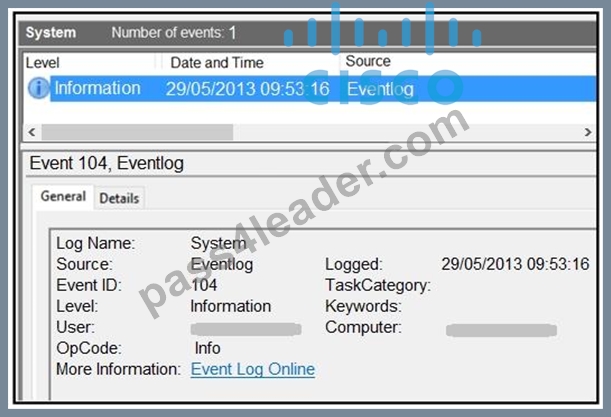
An employee notices unexpected changes and setting modifications on their workstation and creates an incident ticket. A support specialist checks processes and services but does not identify anything suspicious.
The ticket was escalated to an analyst who reviewed this event log and also discovered that the workstation had multiple large data dumps on network shares. What should be determined from this information?
Answer: A
Explanation:
The event log shown in the exhibit isEvent ID 104, which in Windows indicates"The audit log was cleared."This is a significant indicator oflog tampering, a common post-exploitation technique used by attackers to hide their tracks after exfiltrating data or performing unauthorized actions.
The Cisco CyberOps Associate guide mentions:
"Log deletion events, especially Event ID 104, should be treated as potential evidence of malicious activity attempting to cover tracks".
Combined with large data dumps to network shares, this indicates not only unauthorized activity but also deliberate efforts to erase forensic evidence-characteristic oflog tampering.
NEW QUESTION # 111
......
300-215 New Braindumps Free: https://www.pass4leader.com/Cisco/300-215-exam.html
