Now we can say that Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) exam questions are real and top-notch Cisco 300-215 exam questions that you can expect in the upcoming Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) exam. In this way, you can easily pass the 300-215 exam with good scores. The countless 300-215 Exam candidates have passed their dream 300-215 certification exam and they all got help from real, valid, and updated 300-215 practice questions, You can also trust on TrainingDump and start preparation with confidence.
The following will be discussed in CISCO 300-215 exam dumps:
Holding the Cisco 300-215 Certification validates a candidate's expertise in conducting forensic analysis and incident response using Cisco technologies. It also demonstrates the candidate's commitment to advancing their career in cybersecurity and their dedication to staying up-to-date with the latest cybersecurity trends and technologies. Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps certification exam provides an opportunity for professionals to showcase their skills and knowledge in the field and to differentiate themselves from their peers.
>> Best 300-215 Study Material <<
It can be difficult to prepare for the Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) certification test when you're already busy with daily tasks. But, you can successfully prepare for the examination despite your busy schedule if you choose updated and real Cisco 300-215 exam questions. We believe that success in the test depends on studying with Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps (300-215) Dumps questions. We have hired a team of professionals who has years of experience in helping test applicants acquire essential knowledge by providing them with Cisco 300-215 actual exam questions.
This certification test includes five various domains. Each of them focuses on the specific skills that the examinees must develop in advance. The details of these topics are enumerated below:
Fundamentals: This section requires that the candidates demonstrate their competence in performing the following tasks:
NEW QUESTION # 72
Refer to the exhibit.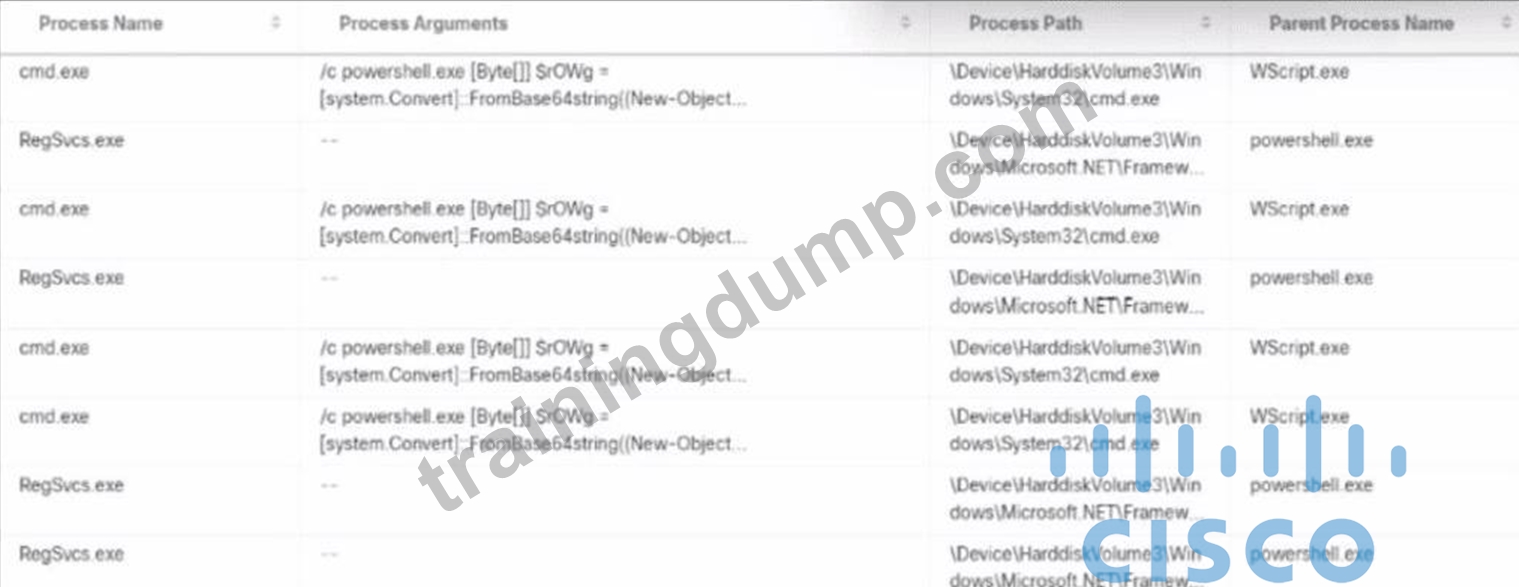
An alert came with a potentially suspicious activity from a machine in HR department. Which two IOCs should the security analyst flag? (Choose two.)
Answer: A,D
Explanation:
The exhibit shows a series of process executions that form a suspicious chain involving scripting engines and obfuscated commands:
* One critical indicator iscmd.exe executing PowerShell with obfuscated (Base64-encoded) arguments
. The use of Base64 is a known method used by attackers to mask malicious commands. This aligns with attack techniques defined under MITRE ATT&CK T1059 (Command and Scripting Interpreter) and T1086 (PowerShell abuse). Therefore, option D is valid.
* Another important IOC isWScript.exe acting as a parent of cmd.exe, which is abnormal in typical business environments. This indicates potential misuse of Windows Script Host (WSH) to launch commands, often seen in phishing or malware dropper scenarios. Thus, option E is also valid.
Options A and B by themselves are not definitive IOCs-PowerShell and cmd.exe are legitimate administrative tools and frequently used in Windows environments.
Option C is not supported by the exhibit-the reverse (powershell.exe initiated by WScript.exe) is what's seen, not the other way around.
These patterns align with theCyberOps Technologies (CBRFIR) 300-215 study guide, which specifies that chaining of interpreters (e.g., WScript # cmd # PowerShell) with encoded commands is a key indicator of compromise during forensic analysis.
Reference:CyberOps Technologies (CBRFIR) 300-215 study guide, Chapter on Identifying Malicious Activity in Host-Based Artifacts and Command-Line Analysis.
NEW QUESTION # 73
An engineer is investigating a ticket from the accounting department in which a user discovered an unexpected application on their workstation. Several alerts are seen from the intrusion detection system of unknown outgoing internet traffic from this workstation. The engineer also notices a degraded processing capability, which complicates the analysis process. Which two actions should the engineer take? (Choose two.)
Answer: A,B
NEW QUESTION # 74
An incident response team is recommending changes after analyzing a recent compromise in which:
a large number of events and logs were involved;
team members were not able to identify the anomalous behavior and escalate it in a timely manner; several network systems were affected as a result of the latency in detection; security engineers were able to mitigate the threat and bring systems back to a stable state; and the issue reoccurred shortly after and systems became unstable again because the correct information was not gathered during the initial identification phase.
Which two recommendations should be made for improving the incident response process? (Choose two.)
Answer: A,D
NEW QUESTION # 75 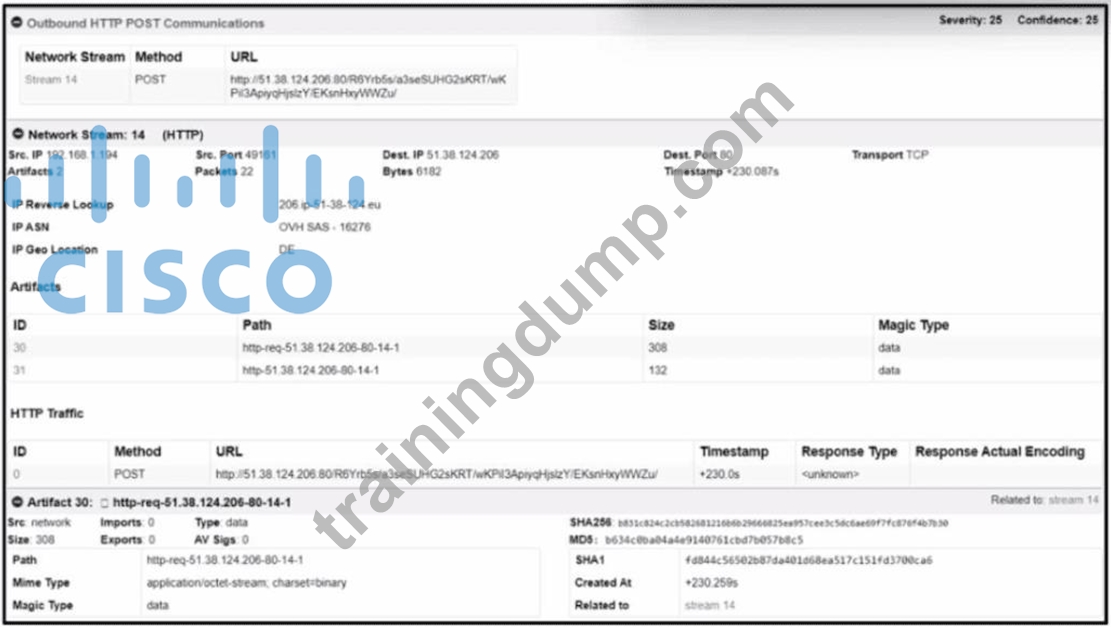
Answer: A
Explanation:
Comprehensive and Detailed Explanation:
From the exhibit, Cisco Secure Malware Analytics (formerly Threat Grid) has captured outbound HTTP POST communication to the IP address 51.38.124.206 on port 80. This destination is highlighted in the analysis under "Outbound HTTP POST Communications," indicating exfiltration behavior or command-and- control (C2) signaling.
Key indicators:
* The report shows that binary data was POSTed to this IP.
* The source system generated 22 packets and sent 6,192 bytes.
* The system has flagged the behavior with a severity of 25 and confidence of 25-suggesting that this is an IoC worth acting on.
Therefore, the artifacts suggest that the destination IP 51.38.124.206 is involved in malicious activity, and the correct answer is:
A: Destination IP 51.38.124.206 is identified as malicious.
NEW QUESTION # 76
Refer to the exhibit.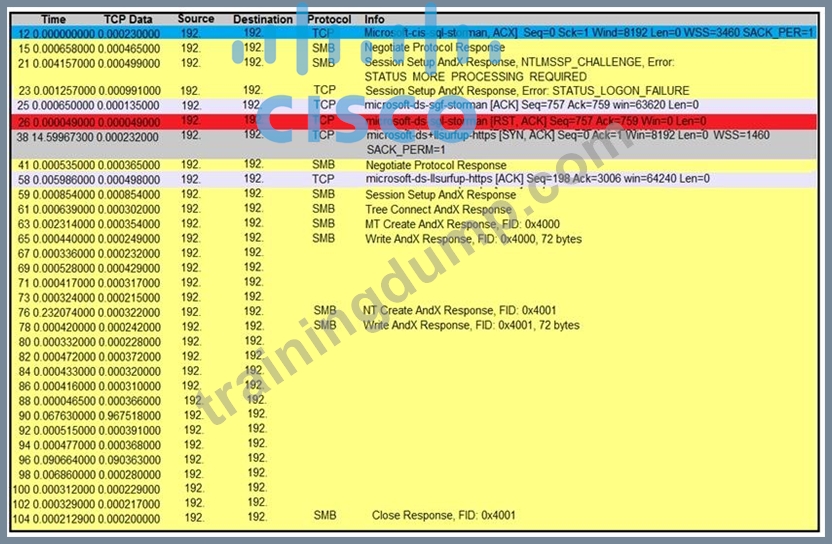
An engineer is analyzing a TCP stream in a Wireshark after a suspicious email with a URL. What should be determined about the SMB traffic from this stream?
Answer: C
NEW QUESTION # 77
......
Free 300-215 Sample: https://www.trainingdump.com/Cisco/300-215-practice-exam-dumps.html
