Itcertmaster Netskope NSK300 exam preparation material is designed to help you pass the Netskope NSK300 exam on your first attempt. The formats mentioned above can be used right away after buying the product. So what are waiting for, get our Netskope Certified Cloud Security Architect (NSK300) study material today and start your constructive progress towards your goals. The rest is assured by us when you give it your all.
It is a common sense that only high quality and accuracy NSK300 practice materials can relive you from those worries. It is our communal wish to reap successful fruits. So our company did a lot to make sure that happen. Our NSK300 practice materials compiled by the most professional experts can offer you with high quality and accuracy results for your success. If you are unfamiliar with our NSK300 practice materials, please download the free demos for your reference, and to some unlearned exam candidates, you can master necessities by our NSK300 practice materials quickly.
>> Trusted NSK300 Exam Resource <<
The meaning of qualifying examinations is, in some ways, to prove the candidate's ability to obtain qualifications that show your ability in various fields of expertise. If you choose our NSK300 study materials, you can create more unlimited value in the limited study time, learn more knowledge, and take the exam that you can take. Through qualifying examinations, this is our NSK300 Study Materials and the common goal of every user, we are trustworthy helpers, so please don't miss such a good opportunity.
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 12
You are deploying the Netskope Client to Windows devices. The following command line would be used to install the client MSI file:
In this scenario, what is <token> referring to in the command line?
Answer: D
Explanation:
In the context of deploying the Netskope Client to Windows devices, <token> in the command line refers to the Netskope organization ID. This is a unique identifier associated with your organization's account within the Netskope security cloud. It is used during the installation process to ensure that client devices are registered and managed under the correct organizational account, enabling appropriate security policies and configurations to beapplied. References: The answer can be inferred from general knowledge about installing software clients and isn't directly available on Netskope's official resources.
NEW QUESTION # 13
A hospital has a patient form that they share with their patients over Gmail. The blank form can be freely shared among anyone. However, if the form has any information filled out. the document is considered confidential.
Which rule type should be used in the DLP profile to match such a document?
Answer: B
Explanation:
The appropriate rule type to use in the DLP profile for a document that is considered confidential when filled out isfingerprint classification. Fingerprinting is a method used to identify and protect sensitive data within documents. It works by creating a digital fingerprint of a file, which can then be used to detect any copies or derivatives of that file.In this case, fingerprinting would allow the hospital to differentiate between the blank patient form, which can be freely shared, and the same form with patient information filled out, which is confidential1.
Netskope's DLP rules can contain elements such as predefined data identifiers, custom data identifiers, keyword identifiers from a dictionary file, RegEx expressions, and exact match criteria1.For this specific use case, fingerprint classification is the most effective method as it can accurately detect the presence of filled- out information in the forms, which is crucial for maintaining patient confidentiality as per HIPAA regulations1.
NEW QUESTION # 14
You are using Netskope CSPM for security and compliance audits across your multi-cloud environments. To decrease the load on the security operations team, you are researching how to auto-re mediate some of the security violations found in low-risk environments.
Which statement is correct in this scenario?
Answer: B
Explanation:
Netskope supports automatic remediation of security violations through its Auto-Remediation frameworks, which are available in the public Netskope GitHub Open Source repository. These frameworks allow for the automatic mitigation of risks associated with security misconfigurations in your cloud environment. The Netskope Auto-Remediation framework for AWS, for example, deploys a set of AWS Lambda functions that query the Netskope API at scheduled intervals and automatically mitigates supported violations1. Similarly, there are frameworks for GCP and other cloud environments that follow the same principle2. This capability is particularly useful for low-risk environments where the security operations team's workload can be reduced by automating the remediation process.
NEW QUESTION # 15
Review the exhibit.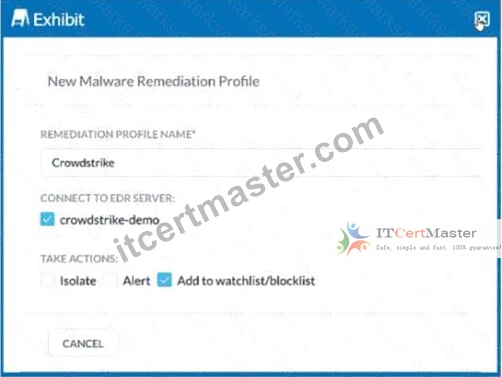
You are asked to integrate Netskope with Crowdstrike EDR. You added the Remediation profile shown in the exhibit.
Which action will this remediation profile take?
Answer: A
NEW QUESTION # 16
A company has deployed Explicit Proxy over Tunnel (EPoT) for their VDI users They have configured Forward Proxy authentication using Okta Universal Directory They have also configured a number of Real- time Protection policies that block access to different Web categories for different AD groups so. for example, marketing users are blocked from accessing gambling sites. During User Acceptance Testing, they see inconsistent results where sometimes marketing users are able to access gambling sites and sometimes they are blocked as expected They are seeing this inconsistency based on who logs into the VDI server first.
What is causing this behavior?
Answer: A
Explanation:
* The inconsistent results observed during User Acceptance Testing (where marketing users sometimes access gambling sites and sometimes are blocked) are likely due to the configuration of the Forward Proxy.
* Cookie Surrogate: The Cookie Surrogate is a mechanism used in Forward Proxy deployments to maintain user context across multiple requests. It ensures that user-specific policies are consistently applied even when multiple users share the same IP address (common in VDI environments).
* Issue: If the Forward Proxy is not configured to use the Cookie Surrogate, it may lead to inconsistent behavior. When different users log into the VDI server, their requests may not be associated with their specific user context, resulting in varying policy enforcement.
* Solution: Ensure that the Forward Proxy is properly configured to use the Cookie Surrogate, allowing consistent policy enforcement based on individual user identities. References:
* Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Training
* Netskope Security Cloud Introductory Online Technical Training
* Netskope Architectural Advantage Features
NEW QUESTION # 17
......
In order to provide users with the most abundant NSK300 learning materials, our company has collected a large amount of information. And set up a professional team to analyze this information. So our NSK300 study questions contain absolutely all the information you need. At the same time, not only you will find the full information in our NSK300 Practice Guide, but also you can discover that the information is the latest and our NSK300 exam braindumps can help you pass the exam for sure just by the first attempt.
NSK300 Exam Sample Online: https://www.itcertmaster.com/NSK300.html
