Itcertkr에서 출시한 Microsoft인증AZ-801 덤프는 시험문제점유율이 가장 높은 시험대비자료입니다. 실제Microsoft인증AZ-801시험문제유형과 같은 형식으로 제작된Microsoft인증AZ-801 시험공부자료로서Itcertkr덤프의 실용가치를 자랑하고 있습니다.덤프를 공부하여 시험불합격하시면 덤프비용은 환불처리해드립니다.
마이크로소프트 아즈러는 가장 인기 있는 클라우드 컴퓨팅 플랫폼 중 하나이며, 모든 규모의 비즈니스에서 널리 사용됩니다. IT 전문가들이 플랫폼을 마스터할 수 있도록, 마이크로소프트는 그들의 기술과 지식을 검증하는 다양한 인증 시험을 제공합니다. 가장 추구되는 인증 중 하나는 AZ-801 (윈도우 서버 하이브리드 고급 서비스 구성) 시험입니다. 이 인증은 윈도우 서버 하이브리드 고급 서비스를 구성하고 관리하고자 하는 IT 전문가들을 위해 설계되었습니다.
Microsoft 인증 AZ-801시험대비덤프를 찾고 계시다면Itcertkr가 제일 좋은 선택입니다.저희Itcertkr에서는 여라가지 IT자격증시험에 대비하여 모든 과목의 시험대비 자료를 발췌하였습니다. Itcertkr에서 시험대비덤프자료를 구입하시면 시험불합격시 덤프비용환불신청이 가능하고 덤프 1년 무료 업데이트서비스도 가능합니다. Itcertkr를 선택하시면 후회하지 않을것입니다.
이 시험을 성공적으로 통과하려면 응시자는 Windows Server, Azure AD, Azure Site Recovery 및 Azure Update Management에 대해 깊이 이해해야합니다. 또한 PowerShell 스크립팅 및 자동화뿐만 아니라 Microsoft 365 서비스 및 테넌트 관리에 익숙해야합니다.
질문 # 48
You plan to deploy the Azure Monitor agent to 100 on-premises servers that run Windows Server.
Which parameters should you provide when you install the agent?
정답:B
설명:
Reference:
https://docs.microsoft.com/en-us/windows-server/storage/storage-spaces/configure-azure-monitor
Topic 2, Fabrikam inc
Case study
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Fabrikam, Inc. is a manufacturing company that has a main office in Chicago and a branch office in Paris.
Existing Environment
Identity Infrastructure
Fabrikam has an Active Directory Domain Services (AD DS) forest that syncs with an Azure Active Directory (Azure AD) tenant. The AD DS forest contains two domains named corp.fabrikam.com and europe.fabrikam.com.
Chicago Office On-Premises Servers
The office in Chicago contains on-premises servers that run Windows Server 2016 as shown in the following table.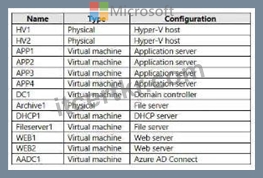
All the servers in the Chicago office are in the corp.fabrikam.com domain.
All the virtual machines in the Chicago office are hosted on HV1 and HV2. HV1 and HV2 are nodes in a failover cluster named Cluster1.
WEB1 and WEB2 run an Internet Information Services (IIS) website. Internet users connect to the website by using a URL of https://www.fabrikam.com.
All the users in the Chicago office run an application that connects to a UNC path of Fileserver1Data.
Paris On-Premises Servers
The office in Paris contains a physical server named dc2.europe.fabrikam.com that runs Windows Server 2016 and is a domain controller for the europe.fabrikam.com domain.
Network Infrastructure
The networks in both the Chicago and Paris offices have local internet connections. The Chicago and Paris offices are connected by using VPN connections.
The client computers in the Chicago office get IP addresses from DHCP1.
Security Risks
Fabrikam identifies the following security risks:
Some accounts connect to AD DS resources by using insecure protocols such as NTLMv1, SMB1, and unsigned LDAP.
Servers have Windows Defender Firewall enabled. Server administrators sometimes modify firewall rules and allow risky connections.
Requirements
Security Requirements
Fabrikam identifies the following security requirements:
Prevent server administrators from configuring Windows Defender Firewalls rules.
Encrypt all the data disks on the servers by using BitLocker Drive Encryption (BitLocker).
Ensure that only authorized applications can be installed or run on the servers in the forest.
Implement Microsoft Sentinel as a reporting solution to identify all connections to the domain controllers that use insecure protocols.
On-Premises Migration Plan
Fabrikam plans to migrate all the existing servers and identifies the following migration requirements:
Move the APP1 and APP2 virtual machines in the Chicago office to a new Hyper-V failover cluster named Cluster2 that will run Windows Server 2022.
Cluster2 will contain two new nodes named HV3 and HV4.
All virtual machine files will be stored on a Cluster Shared Volume (CSV).
Migrate Archive1 to a new failover cluster named Cluster3 that will run Windows Server 2022.
Cluster3 will contain two physical nodes named Node1 and Node2.
The file shares on Cluster3 will be a failover cluster role in active-passive mode.
Migrate all users, groups, and client computers from europe.fabrikam.com to corp.fabrikam.com.
The migration will be performed by using the Active Directory Migration Tool (ADMT).
A computer named ADMTcomputer will be deployed to the corp.fabrikam.com domain to run ADMT migration procedures.
User accounts will retain their existing password.
Migrate the data share from Fileserver1 to a new server named Fileserver2 that will run Windows Server
2022. After the migration, the data share must be accessible by using the existing UNC path.
Azure Migration Plan
Fabrikam plans to migrate some resources to Azure and identifies the following migration requirements:
Create an Azure subscription named Sub1.
Create an Azure virtual network named Vnet1.
Use ExpressRoute to connect the Paris and Chicago offices to Vnet1.
License all servers for Microsoft Defender for servers.
Migrate APP3 and APP4 to Azure.
Migrate the www.fabrikam.com website to an Azure App Service web app named WebApp1.
Decommission WEB1 and WEB2.
DHCP Migration Plan
Fabrikam plans to replace DHCP1 with a new server named DHCP2 and identifies the following migration requirements:
Ensure that DHCP2 provides the same IP addresses that are currently available from DHCP1.
Prevent DHCP1 from servicing clients once services are enabled on DHCP2.
Ensure that the existing leases and reservations are migrated.
질문 # 49
You manage 200 physical servers that run Windows Server.
You plan to migrate the servers to Azure.
You need to prepare for discovery of the servers by using Azure Migrate.
Which three actions should you perform in sequence on a physical server? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.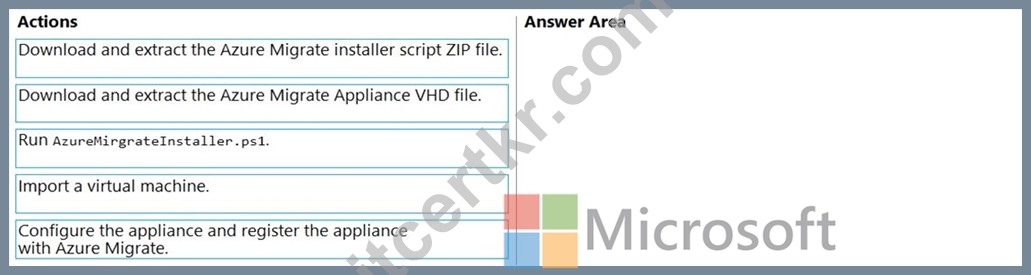
정답:
설명: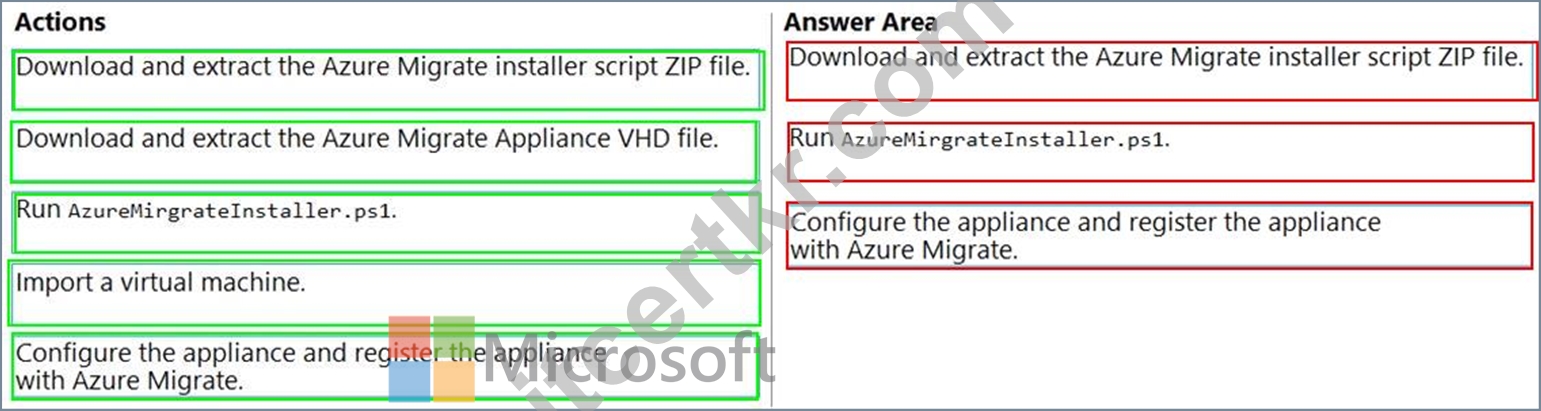
Reference:
https://docs.microsoft.com/en-us/azure/migrate/tutorial-discover-physical
질문 # 50
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a server named Server1 that runs Windows Server.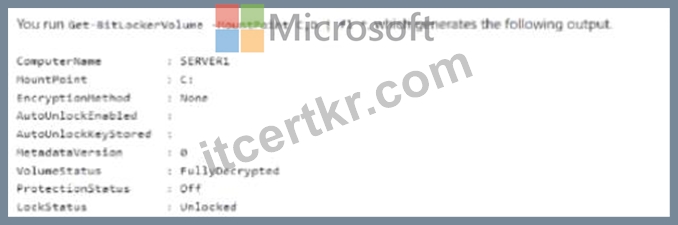
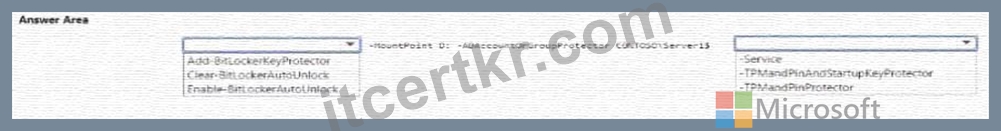
정답:
설명: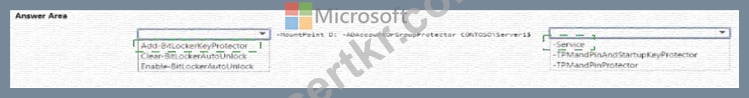
Explanation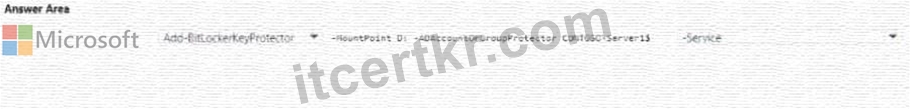
질문 # 51
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a failover cluster named Cluster1.
You need to configure Cluster-Aware Updating (CAU) on the cluster by using Windows Admin Center (WAC).
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.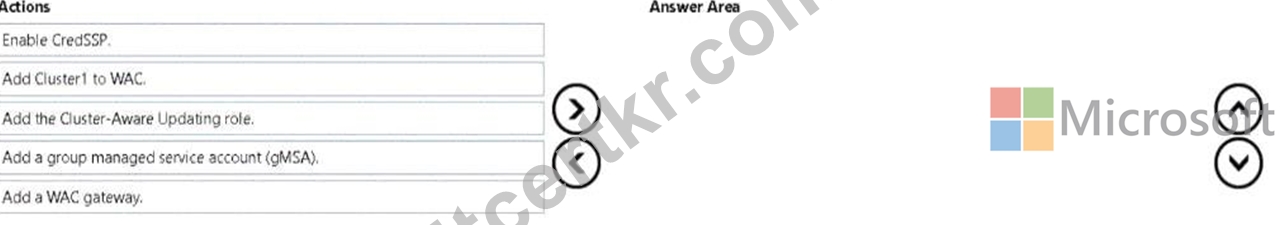
정답:
설명: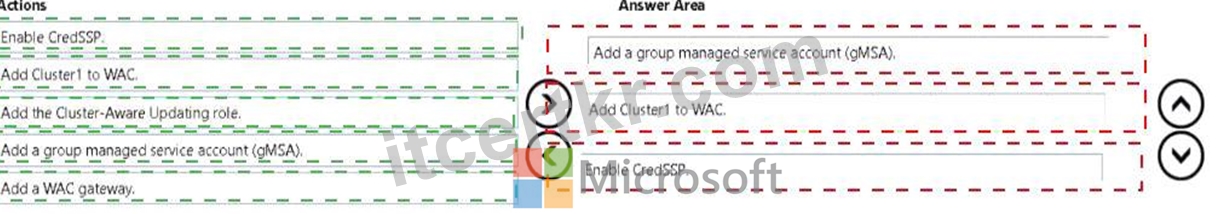
Explanation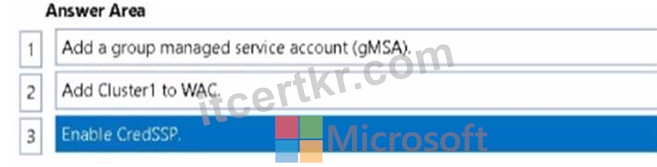
질문 # 52
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains three servers named Server1, Server2, and Server3 that run Windows Server. All the servers are on the same network and have network connectivity.
On Server1, Windows Defender Firewall has a connection security rule that has the following settings:
* Rule Type: Server-to-server
* Endpoint 1: Any IP address
* Endpoint 2: Any IP address
* Requirements: Require authentication for inbound connections and request authentication for outbound connections
* Authentication Method: Computer (Kerberos V5)
* Profile: Domain, Private, Public
* Name: Rule1
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.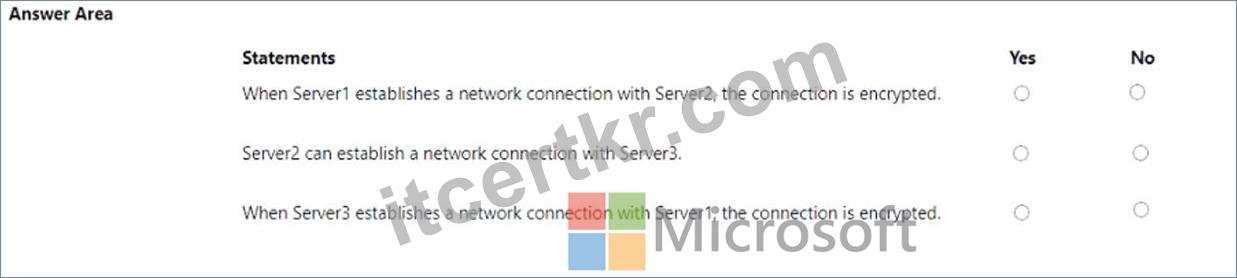
정답:
설명: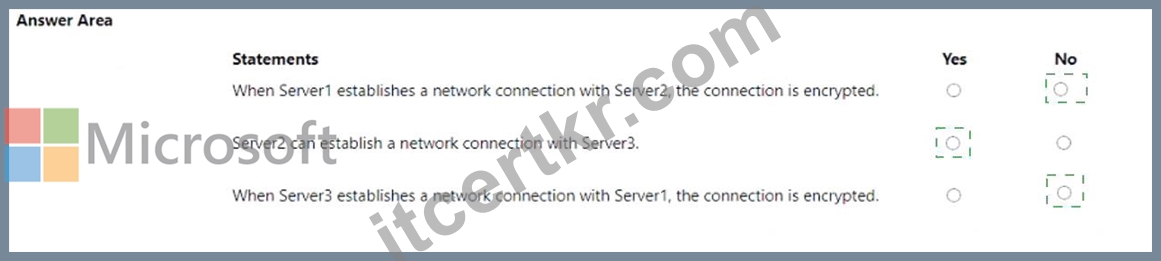
Explanation: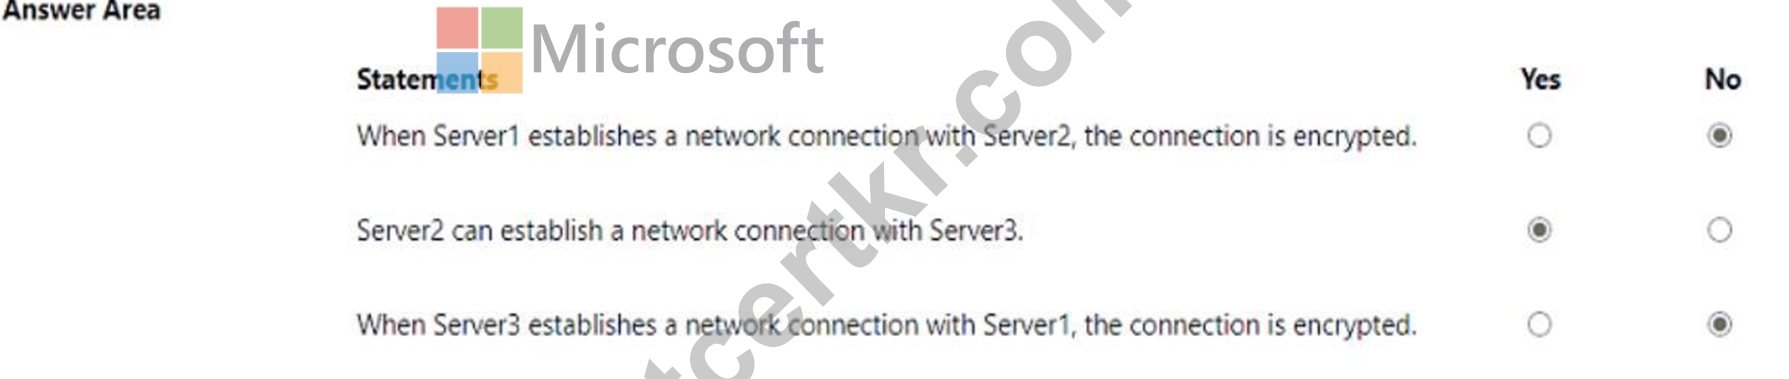
질문 # 53
......
AZ-801유효한 시험덤프: https://www.itcertkr.com/AZ-801_exam.html
