We provide you with two kinds of consulting channels if you are confused about some questions on our IdentityNow-Engineer study materials. You can email us or contact our online customer service. We will reply you as soon as possible. You are free to ask questions about IdentityNow-Engineer training prep at any time since that we are working 24/7 online. Our staff is really very patient and friendly. They are waiting to give you the most professional suggestions on our IdentityNow-Engineer exam questions.
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
>> IdentityNow-Engineer Latest Test Experience <<
However, when asked whether the IdentityNow-Engineer latest dumps are reliable, costumers may be confused. For us, we strongly recommend the IdentityNow-Engineer exam questions compiled by our company, here goes the reason. On one hand, our IdentityNow-Engineer test material owns the best quality. When it comes to the study materials selling in the market, qualities are patchy. But our SailPoint test material has been recognized by multitude of customers, which possess of the top-class quality, can help you pass exam successfully. On the other hand, our IdentityNow-Engineer Latest Dumps are designed by the most experienced experts, thus it can not only teach you knowledge, but also show you the method of learning in the most brief and efficient ways.
NEW QUESTION # 104
Is this statement correct about security and/or encryption of data?
Solution: identityNow uses a hashing algorithm for secure encryption of data in transit and uses TLS for hashing passwords and the answers to security questions
Answer: B
Explanation:
No, this statement is incorrect. While IdentityNow does use TLS (Transport Layer Security) for securing data in transit, TLS is not a hashing algorithm; it is a protocol used for encryption to ensure secure communication over networks. Additionally, IdentityNow uses hashing algorithms for securely storing passwords and answers to security questions (e.g., SHA-256 or bcrypt), but it does not use TLS for hashing these values. Hashing algorithms are one-way functions that help store sensitive data securely by converting them into irreversible fixed-length representations.
TLS protects data during transmission by encrypting it, while hashing is used for securing stored data such as passwords.
References:
* SailPoint IdentityNow Encryption and Security Practices Documentation.
* SailPoint IdentityNow Password Hashing and Encryption Mechanisms Guide.
NEW QUESTION # 105
An IdentityNow engineer has set up an access profile for an application. The access profile allows for users to request access, and for a user's manager to approve or deny access.
After a recent staff meeting, management has expressed that they want to remove any approval requirements for this application.
Is management's request possible in IdentityNow. and. if so. are these the recommended steps the engineer should take to meet their new requirement?
Solution: It is possible. Delete the certification campaign associated with this application.
Answer: B
Explanation:
No, deleting the certification campaign associated with the application is not the correct step to remove approval requirements for an access request. Certification campaigns are related to periodic reviews of access, not the approval workflow for access requests. To remove the manager approval requirement, changes should be made to the access profile or the associated workflow, not the certification campaign.
Key Reference from SailPoint Documentation:
* Certification Campaigns: Certification campaigns are used for access reviews and do not control approval workflows for access requests.
NEW QUESTION # 106
Is the following true about custom connectors in IdentityNow?
Solution: Custom connector configurations can have account correlation settings defined.
Answer: A
Explanation:
Yes, custom connector configurations in SailPoint IdentityNow can have account correlation settings defined. Account correlation is used to link accounts from different sources to the correct identity in IdentityNow. When configuring a custom connector, it is possible to define how accounts from the connected system are correlated to existing identities based on attributes like usernames or other unique identifiers.
Key Reference from SailPoint Documentation:
* Custom Connector Configuration: SailPoint allows for the definition of account correlation settings in custom connectors to ensure proper linking of external accounts to internal identities.
NEW QUESTION # 107
Refer to the following diagram.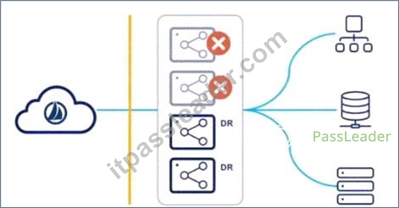
For this strategy, all virtual appliances (VAs) are deployed in a single VA cluster, with all VAs running concurrently. Some of these VAs are in the primary data center, and others {called OR VAs) are deployed in a DR data center.
While using this strategy, is this a disadvantage?
Solution: A reconfiguration will be required within identityNow to connect to the disaster recovery VAs. If there are many sources configured, this will cause overhead in performing this failover
Answer: B
Explanation:
No, reconfiguration within IdentityNow is not required to connect to the disaster recovery (DR) VAs, which makes this scenario not a disadvantage. When properly configured, all VAs (including DR VAs) in a cluster are part of the same logical unit, meaning that failover to the DR VAs should happen seamlessly without manual intervention or significant reconfiguration. IdentityNow handles the failover automatically, directing traffic to the DR VAs when primary VAs become unavailable.
While there might be some overhead in a manual failover scenario for certain configurations, the use of a single VA cluster helps mitigate this by ensuring the system can failover without needing complex reconfigurations for every source.
References:
* SailPoint IdentityNow Virtual Appliance Failover and Disaster Recovery Configuration.
* SailPoint IdentityNow High Availability Architecture Guide.
NEW QUESTION # 108
The customer has a system that matches the following description. Is this a suitable connector type to use?
The system is a modern, cloud-based, web application that uses a MySQL database backend provided by the cloud platform. The database is only accessible from the web application. The web application exposes a fully compliant SCIM 2.0 interface with OAuth 2.0 client credentials.
Solution: OpenLDAP Connector
Answer: B
Explanation:
No, the OpenLDAP Connector is not suitable for this use case. OpenLDAP is designed for integrating with LDAP-based directories, and the system described is a cloud-based web application that uses a SCIM 2.0 interface with OAuth 2.0 for authentication. Since the system supports SCIM, the correct connector would be the SCIM 2.0 Connector, which is tailored for cloud-based systems with SCIM interfaces.
References:
SailPoint IdentityNow OpenLDAP Connector Guide.
SailPoint IdentityNow SCIM 2.0 Connector Documentation.
NEW QUESTION # 109
......
ITPassLeader wants to win the trust of SailPoint Certified IdentityNow Engineer (IdentityNow-Engineer) exam candidates at any cost. To achieve this objective ITPassLeader is offering real, updated, and error-free SailPoint Certified IdentityNow Engineer (IdentityNow-Engineer) exam dumps in three different formats. These SailPoint Certified IdentityNow Engineer (IdentityNow-Engineer) exam questions formats are ITPassLeader SailPoint IdentityNow-Engineer dumps PDF files, desktop practice test software, and web-based practice test software.
IdentityNow-Engineer New Exam Bootcamp: https://www.itpassleader.com/SailPoint/IdentityNow-Engineer-dumps-pass-exam.html
