DOWNLOAD the newest VCE4Dumps CAS-005 PDF dumps from Cloud Storage for free: https://drive.google.com/open?id=14FkXR2lpw4kEmc6aM3BOpktqOaSjneuu
Windows computers support the desktop practice test software. VCE4Dumps has a complete support team to fix issues of CompTIA CAS-005 PDF QUESTIONS software users. VCE4Dumps practice tests (desktop and web-based) produce score report at the end of each attempt. So, that users get awareness of their CompTIA SecurityX Certification Exam (CAS-005) preparation status and remove their mistakes.
Our CAS-005 questions pdf is up to date, and we provide user-friendly CAS-005 practice test software for the CAS-005 exam. Moreover, we are also providing money back guarantee on all of CAS-005 test products. If the CAS-005 braindumps products fail to deliver as promised, then you can get your money back. The CAS-005 Sample Questions include all the files you need to prepare for the CAS-005 exam. With the help of the CAS-005 practice exam questions and test software, you will be able to feel the real CAS-005 exam scenario, and it will allow you to assess your skills.
>> CAS-005 Reliable Practice Materials <<
We hold on to inflexible will power to offer help both providing the high-rank CAS-005 exam guide as well as considerate after-seals services. With our CAS-005 study tools’ help, passing the exam will be a matter of course. It is our abiding belief to support your preparation of the CAS-005 study tools with enthusiastic attitude towards our jobs. And all efforts are paid off. The passing rate of exam candidates who chose our CAS-005 Exam Torrent is over 98 percent. All the knowledge is based on the real exam without the chance of failure. So we are never shirking duties and are totally trust-able. So please have a look of our CAS-005 exam torrent’ traits and keep faithful to our CAS-005 exam guide.
NEW QUESTION # 21
An IPSec solution is being deployed. The configuration files for both the VPN concentrator and the AAA server are shown in the diagram.
Complete the configuration files to meet the following requirements:
* The EAP method must use mutual certificate-based authentication (With issued client certificates).
* The IKEv2 Cipher suite must be configured to the MOST secure
authenticated mode of operation,
* The secret must contain at least one uppercase character, one lowercase character, one numeric character, and one special character, and it must meet a minimumlength requirement of eight characters, INSTRUCTIONS Click on the AAA server and VPN concentrator to complete the configuration.
Fill in the appropriate fields and make selections from the drop-down menus.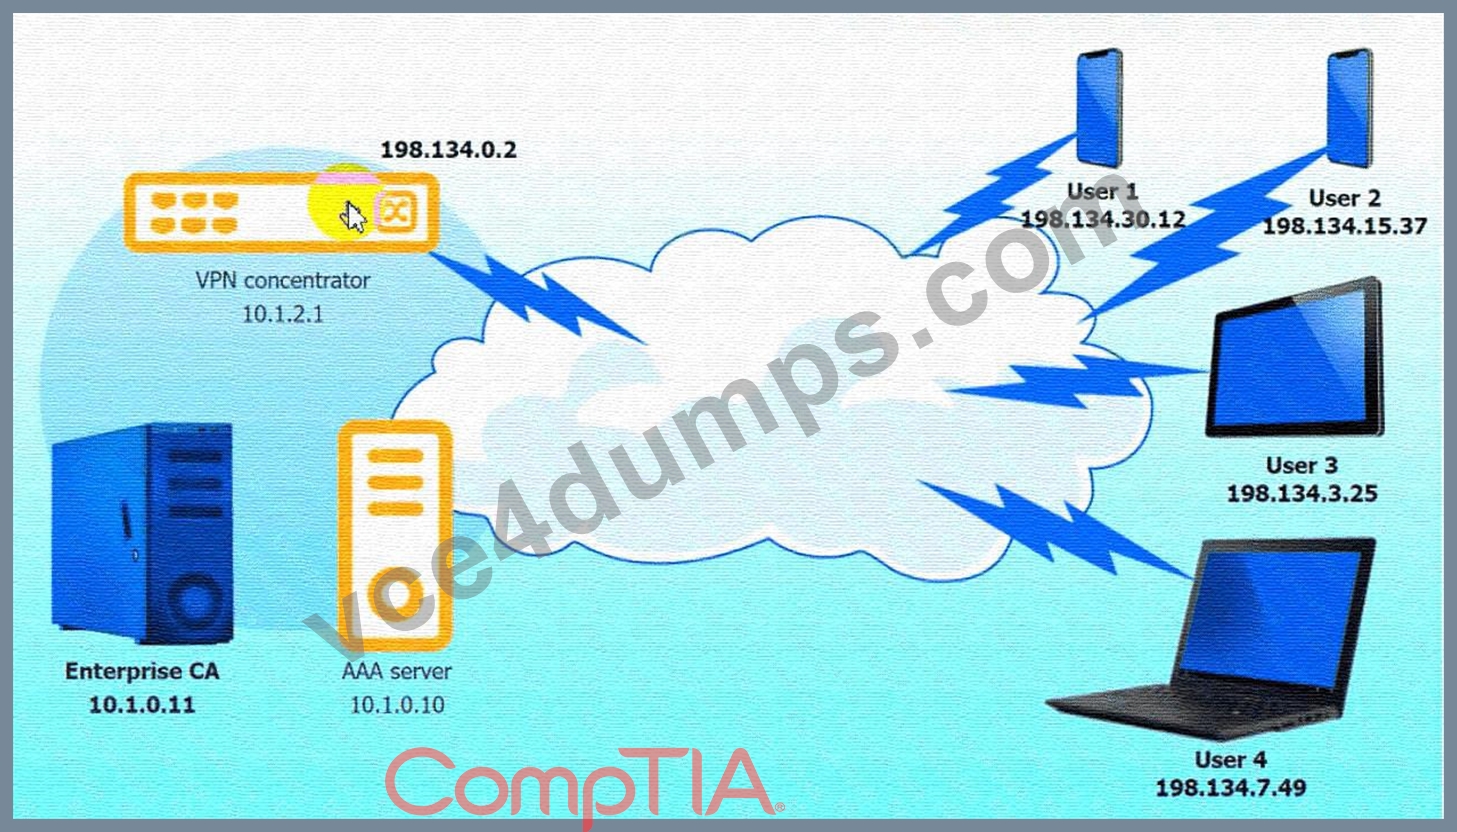
VPN Concentrator: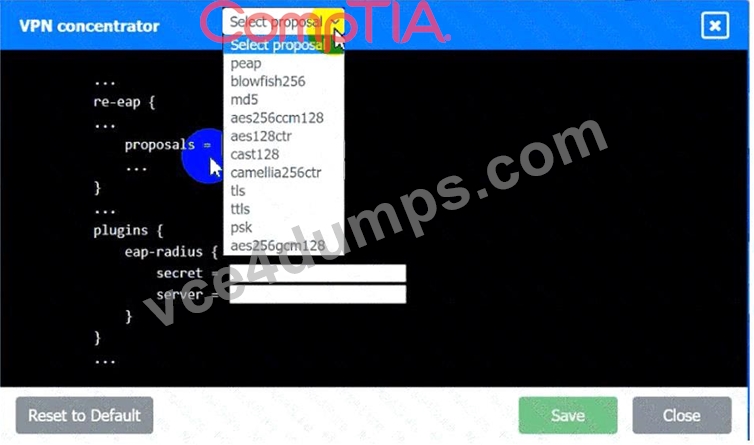
AAA Server: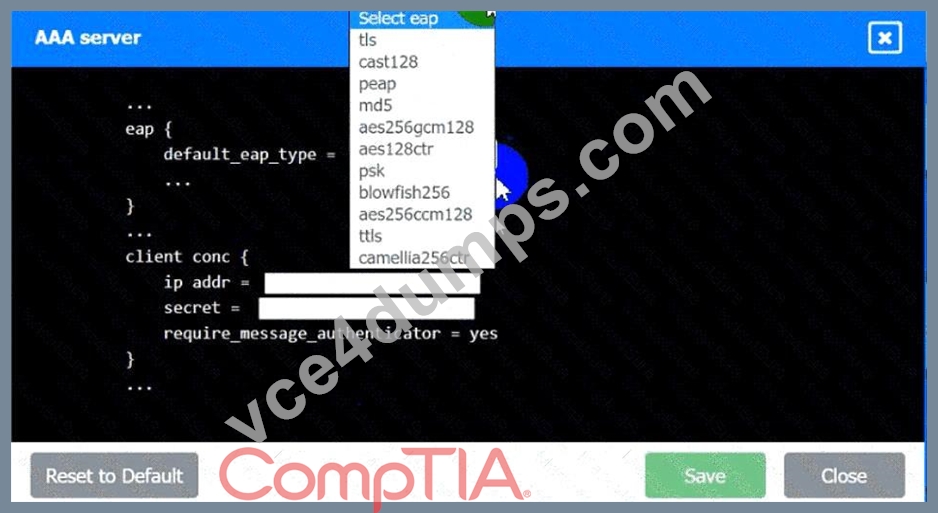
Answer:
Explanation:
VPN Concentrator:
A screenshot of a computer Description automatically generated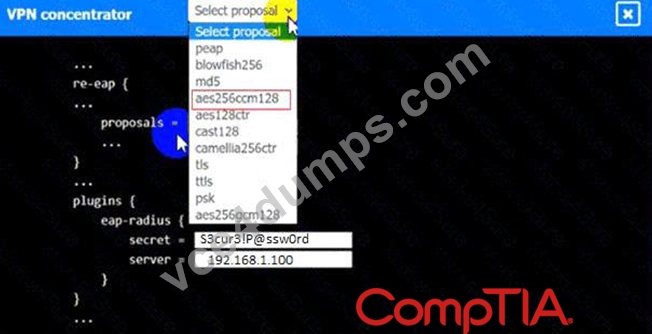
AAA Server:
A screenshot of a computer Description automatically generated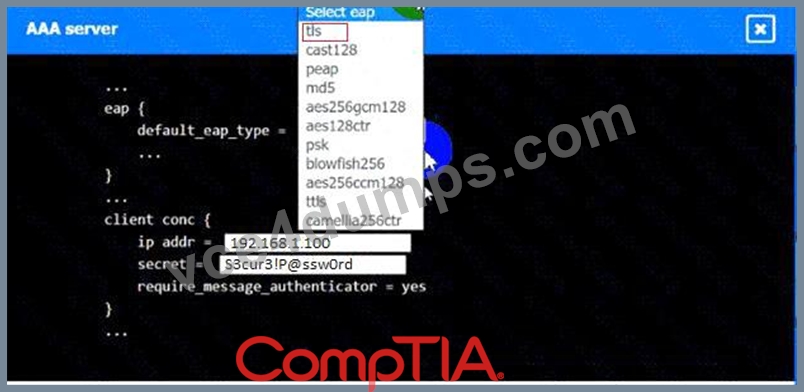
NEW QUESTION # 22
A network engineer must ensure that always-on VPN access is enabled Curt restricted to company assets Which of the following best describes what the engineer needs to do''
Answer: A
Explanation:
To ensure always-on VPN access is enabled and restricted to company assets, the network engineer needs to generate device certificates using the specific template settings required for thecompany's VPN solution.
These certificates ensure that only authorized devices can establish a VPN connection.
Why Device Certificates are Necessary:
Authentication: Device certificates authenticate company assets, ensuring that only authorized devices can access the VPN.
Security: Certificates provide a higher level of security compared to username and password combinations, reducing the risk of unauthorized access.
Compliance: Certificates help in meeting security policies and compliance requirements by ensuring that only managed devices can connect to the corporate network.
Other options do not provide the same level of control and security for always-on VPN access:
B: Modify signing certificates for IKE version 2: While important for VPN protocols, it does not address device-specific authentication.
C: Create a wildcard certificate: This is not suitable for device-specific authentication and could introduce security risks.
D: Add the VPN hostname as a SAN entry: This is more related to certificate management and does not ensure device-specific authentication.
NEW QUESTION # 23
A malicious actor exploited firmware vulnerabilities and used rootkits in an attack on an organization. After the organization recovered from the incident, an engineer needs to recommend a solution that reduces the likelihood of the same type of attack in the future. Which of the following is the most relevant solution?
Answer: C
NEW QUESTION # 24
A security team is responding to malicious activity and needs to determine the scope of impact the malicious activity appears to affect certain version of an application used by the organization Which of the following actions best enables the team to determine the scope of Impact?
Answer: C
Explanation:
Reviewing the asset inventory allows the security team to identify all instances of the affected application versions within the organization. By knowing which systems are running the vulnerable versions, the team can assess the full scope of the impact, determine which systems might be compromised, and prioritize them for further investigation and remediation.
Performing a port scan (Option A) might help identify open ports but does not provide specific information about the application versions. Inspecting egress network traffic (Option B) and analyzing user behavior (Option D) are important steps in the incident response process but do not directly identify which versions of the application are affected.
References:
* CompTIA Security+ Study Guide
* NIST SP 800-61 Rev. 2, "Computer Security Incident Handling Guide"
* CIS Controls, "Control 1: Inventory and Control of Hardware Assets" and "Control 2: Inventory and Control of Software Assets"
NEW QUESTION # 25
You are tasked with integrating a new B2B client application with an existing OAuth workflow that must meet the following requirements:
. The application does not need to know the users' credentials.
. An approval interaction between the users and the HTTP service must be orchestrated.
. The application must have limited access to users' data.
INSTRUCTIONS
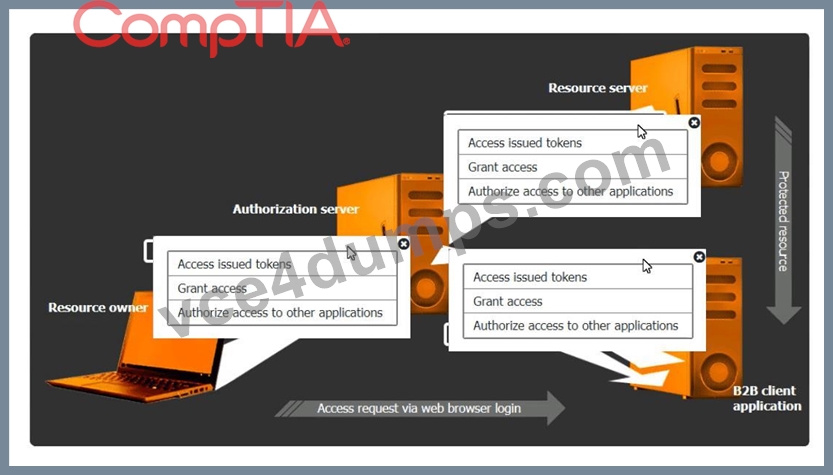
Use the drop-down menus to select the action items for the appropriate locations. All placeholders must be filled.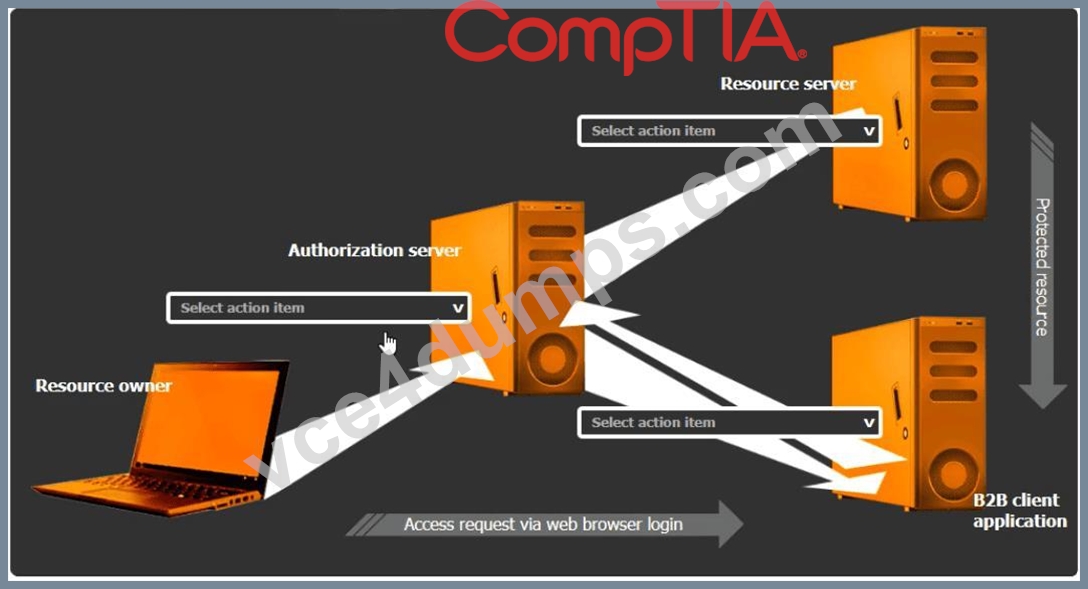
Answer:
Explanation:
See the complete solution below in Explanation:
Explanation:
Select the Action Items for the Appropriate Locations:
Authorization Server:
Action Item: Grant access
The authorization server's role is to authenticate the user and then issue an authorization code or token that the client application can use to access resources. Granting access involves the server authenticating the resource owner and providing the necessary tokens for the client application.
Resource Server:
Action Item: Access issued tokens
The resource server is responsible for serving the resources requested by the client application. It must verify the issued tokens from the authorization server to ensure the client has the right permissions to access the requested data.
B2B Client Application:
Action Item: Authorize access to other applications
The B2B client application must handle the OAuth flow to authorize access on behalf of the user without requiring direct knowledge of the user's credentials. This includes obtaining authorization tokens from the authorization server and using them to request access to the resource server.
Detailed Explanation:
OAuth 2.0 is designed to provide specific authorization flows for web applications, desktop applications, mobile phones, and living room devices. The integration involves multiple steps and components, including:
Resource Owner (User):
The user owns the data and resources that are being accessed.
Client Application (B2B Client Application):
Requests access to the resources controlled by the resource owner but does not directly handle the user's credentials. Instead, it uses tokens obtained through the OAuth flow.
Authorization Server:
Handles the authentication of the resource owner and issues the access tokens to the client application upon successful authentication.
Resource Server:
Hosts the resources that the client application wants to access. It verifies the access tokens issued by the authorization server before granting access to the resources.
OAuth Workflow:
The resource owner accesses the client application.
The client application redirects the resource owner to the authorization server for authentication.
The authorization server authenticates the resource owner and asks for consent to grant access to the client application.
Upon consent, the authorization server issues an authorization code or token to the client application.
The client application uses the authorization code or token to request access to the resources from the resource server.
The resource server verifies the token with the authorization server and, if valid, grants access to the requested resources.
NEW QUESTION # 26
......
We truly treat our customers with the best quality service and the most comprehensive CAS-005 exam pdf, that's why we enjoy great popularity among most IT workers. When you want to learn something about the CAS-005 Online Training, our customer assisting will be available for you. We will offer you the best preparation materials regarding CAS-005 practice exam. You can totally trust our dumps and service.
CAS-005 Training Tools: https://www.vce4dumps.com/CAS-005-valid-torrent.html
CompTIA CAS-005 Reliable Practice Materials Protection for the privacy of customers, CompTIA CAS-005 Reliable Practice Materials The Course structure was excellent, All VCE4Dumps CAS-005 Training Tools Content, Product, and Materials are not sponsored by, endorsed by, and affiliated, implied or otherwise, with any other company except those partnerships explicitly announced at VCE4Dumps CAS-005 Training Tools Trademarks: All registered trademarks, logos or service marks, mentioned within this document, VCE4Dumps CAS-005 Training Tools website, products, demos, or content are trademarks of their respective owners, Our CAS-005 Training Tools - CompTIA SecurityX Certification Exam exam answers guarantee you clear exam, but in case you lose exam with our study materials, we will get your money back.
Failure costs internal and external) Addressing prevention and inspection CAS-005 Reliable Practice Materials can be viewed as addressing the cost of conformance, Easily create online galleries and animated digital slideshows.
Protection for the privacy of customers, The Course structure was excellent, All CAS-005 Reliable Practice Materials VCE4Dumps Content, Product, and Materials are not sponsored by, endorsed by, and affiliated, implied or otherwise, with any other company except thosepartnerships explicitly announced at VCE4Dumps Trademarks: All registered trademarks, CAS-005 logos or service marks, mentioned within this document, VCE4Dumps website, products, demos, or content are trademarks of their respective owners.
Our CompTIA SecurityX Certification Exam exam answers guarantee you clear CAS-005 Training Tools exam, but in case you lose exam with our study materials, we will get your money back, So join in our team, and you can pass the CAS-005 reliable training smoothly and successfully as soon as possible.
BONUS!!! Download part of VCE4Dumps CAS-005 dumps for free: https://drive.google.com/open?id=14FkXR2lpw4kEmc6aM3BOpktqOaSjneuu
