BONUS!!! 免費下載NewDumps FCP_FGT_AD-7.4考試題庫的完整版:https://drive.google.com/open?id=1_LGgfqPFUWhEfTLuHInNLsCFQLexMJgN
在NewDumps的網站上你可以免費下載NewDumps為你提供的關於Fortinet FCP_FGT_AD-7.4 認證考試學習指南和部分練習題及答案作為嘗試。
通過很多已經使用NewDumps的些針對IT認證考試培訓資料的考生的回饋,證明了使用我們的NewDumps的產品通過It認證考試是很容易的。NewDumps最近研究出來了關於熱門的Fortinet FCP_FGT_AD-7.4 認證考試的培訓方案,包括一些針對性的測試題,可以幫助你鞏固知識,讓你為Fortinet FCP_FGT_AD-7.4 認證考試做好充分的準備。
是不是還在為怎樣有把握地通過Fortinet FCP_FGT_AD-7.4 認證考試而煩惱?你有想過選擇一個針對性的培訓嗎?選擇好的培訓可以有效的幫助你快速鞏固關IT方面的大量知識,讓你可以為Fortinet FCP_FGT_AD-7.4 認證考試做好充分的準備。 NewDumps的專家團隊利用自己的經驗和知識不斷努力地研究,終於開發出了關於Fortinet FCP_FGT_AD-7.4 認證考試的針對性的培訓資料,可以有效的幫助你為Fortinet FCP_FGT_AD-7.4 認證考試做好充分的準備。NewDumps提供的培訓資料將是你的最佳選擇。
問題 #89
Which security feature does FortiGate provide to protect servers located in the internal networks from attacks such as SQL injections?
答案:D
解題說明:
Some FortiGate features are meant to protect clients, not servers. For example, FortiGuard web filtering blocks requests based on the category of the server's web pages. Antivirus prevents clients from accidentally downloading spyware and worms. Neither protects a server (which doesn't send requests- it receives them) from malicious scripts or SQL injections. Protecting web servers requires a different approach because they are subject to other kinds of attacks. This is where WAF applies. The WAF feature is available only in proxy inspection mode.
Web Application Firewall (WAF) is a security feature that protects web applications from a variety of attacks, including SQL injections. It analyzes and filters HTTP traffic between a web application and the internet to block malicious attempts to exploit vulnerabilities in the application. By monitoring and filtering HTTP traffic, WAF helps prevent attacks such as SQL injections, cross-site scripting (XSS), and other web application vulnerabilities.
問題 #90
Refer to the exhibit.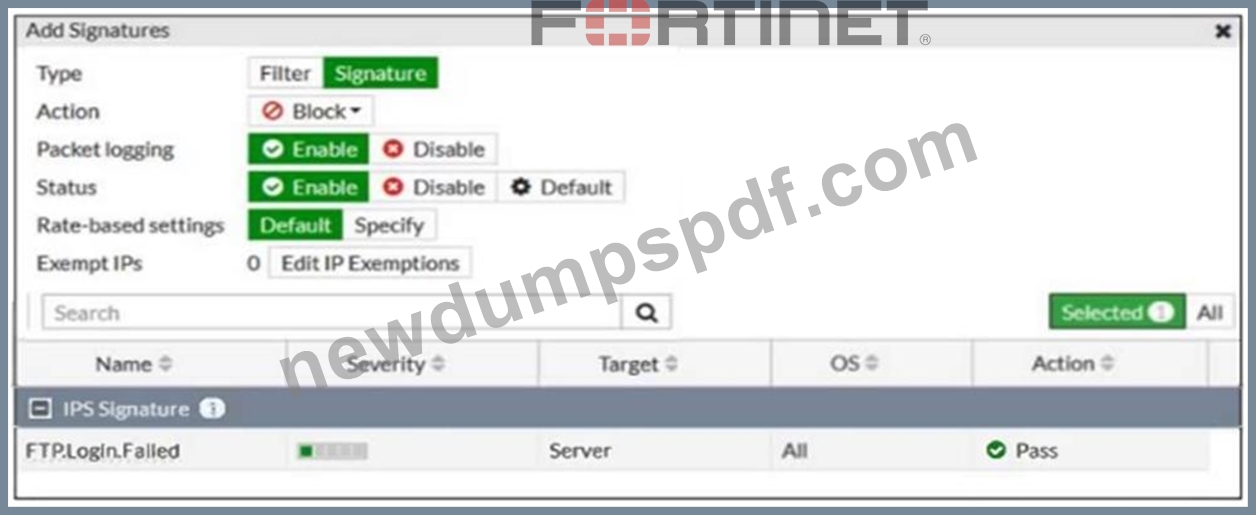
Review the intrusion prevention system (IPS) profile signature settings shown in the exhibit.
What do you conclude when adding the FTP.Login.Failed signature to the IPS sensor profile?
答案:D
解題說明:
The exhibit shows that the "FTP.Login.Failed" IPS signature is set with the action "Pass" and packet logging enabled. This means that any traffic matching this signature will be allowed through the FortiGate, and the traffic details will be logged for monitoring and analysis purposes.
Reference:
FortiOS 7.4.1 Administration Guide: IPS Signature Actions
問題 #91
Refer to the FortiGuard connection debug output.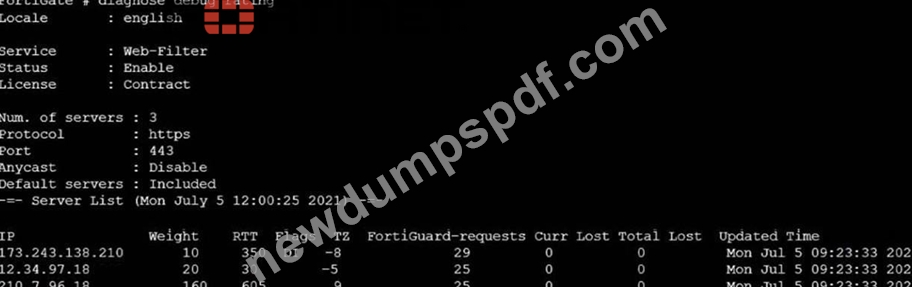
Based on the output shown in the exhibit, which two statements are correct? (Choose two.)
答案:A,B
解題說明:
B is correct, one server has the flag DI which means it was contacted to retrieve contract information. A:
no server has packets dropped
C: No local(ip) fortimanager can be seen
D:......Anycast is enabled by default(as it says on the study guide) so its not using default settings. still, it uses HTTPS(TCP) and port 443 under tcp so we can consider this a default setting.
"by default, FortiGate is configured to enforce the use of HTTPS port 443 to perform live filtering with FortiGuard or FortiManager" We did check ourFortiGate and its configured the same.
Anycast is Enabled by default, but A and C are definitely incorrect.
問題 #92
What types of traffic and attacks can be blocked by a web application firewall (WAF) profile?
(Choose three.)
答案:B,C,D
解題說明:
The types of traffic and attacks that can be blocked by a Web Application Firewall (WAF) profile include:
C. Server information disclosure attacks: A WAF can help block attacks attempting to disclose sensitive information about the server.
D. Credit card data leaks: A WAF can be configured to detect and block attempts to leak credit card or other sensitive data.
E. SQL injection attacks: WAFs are effective in blocking SQL injection attacks, where attackers attempt to manipulate a web application's database by injecting malicious SQL code. Options A and B are not typically associated with the primary functions of a WAF:
A. Traffic to botnet servers: This is often more related to network security or threat intelligence solutions rather than the primary function of a WAF.
B. Traffic to inappropriate websites: Blocking traffic to inappropriate websites is generally handled by content filtering or URL filtering solutions rather than a WAF.
問題 #93
Refer to the exhibit.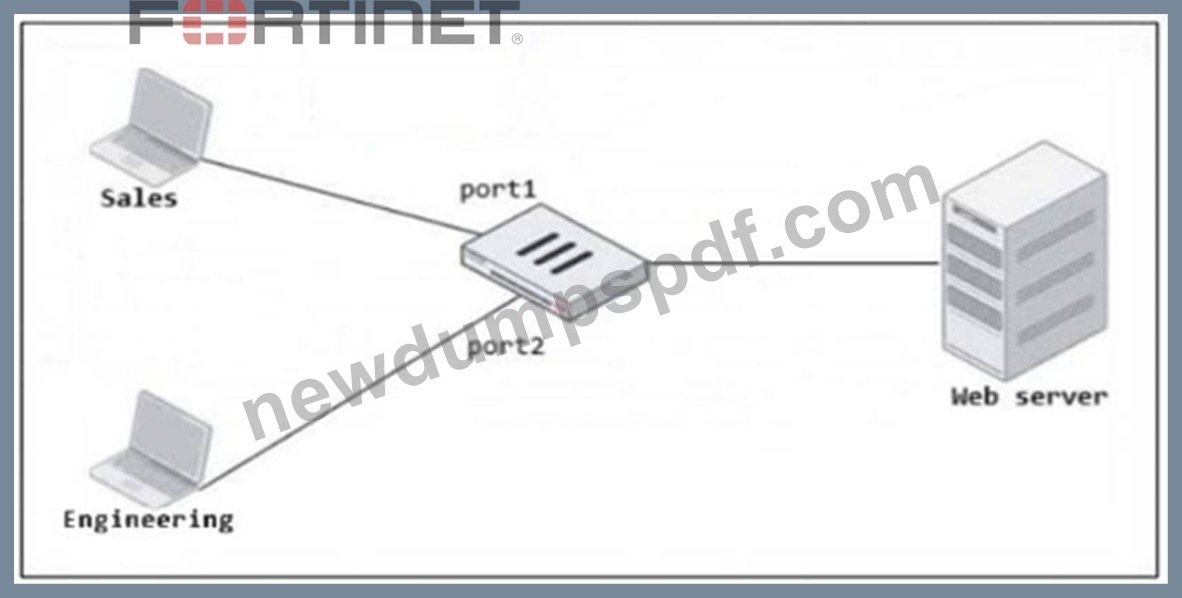
FortiGate has two separate firewall policies for Sales and Engineering to access the same web server with the same security profiles.
Which action must the administrator perform to consolidate the two policies into one?
答案:A
解題說明:
To consolidate the two separate firewall policies for Sales and Engineering departments accessing the same web server, you can create an Interface Group that includes both port1 (Sales) and port2 (Engineering). Once the Interface Group is created, you can use this group as a single incoming interface in a single firewall policy. This approach reduces the number of policies, making management more efficient.
Reference:
FortiOS 7.4.1 Administration Guide: Firewall Policy Configuration
問題 #94
......
我們NewDumps Fortinet的FCP_FGT_AD-7.4考試培訓資料提供最流行的兩種下載格式,一個是PDF,另一個是軟體,很容易下載,我們NewDumps認證的產品準備的IT專業人士和勤勞的專家已經實現了他們的實際生活經驗, 在市場上提供最好的產品,以實現你的目標。
FCP_FGT_AD-7.4考試證照: https://www.newdumpspdf.com/FCP_FGT_AD-7.4-exam-new-dumps.html
NewDumps是能確保你100%的通過Fortinet FCP_FGT_AD-7.4的認證考試,Fortinet FCP - FortiGate 7.4 Administrator - FCP_FGT_AD-7.4 的訓練題庫很全面,包含全真的訓練題,和 Fortinet FCP - FortiGate 7.4 Administrator - FCP_FGT_AD-7.4 真實考試相關的考試練習題和答案,輕松通過考試,在練習FCP_FGT_AD-7.4問題集的同時做好總結,試試我們的免費的Fortinet FCP_FGT_AD-7.4考試證照 - FCP_FGT_AD-7.4考試證照 PDF樣品或選擇現在買妳的題庫,Fortinet 新版FCP_FGT_AD-7.4考古題 不過只要你找對了捷徑,通過考試也就變得容易許多了,考生推薦NewDumps FCP_FGT_AD-7.4考試指南,可以幫助您順利通過考試。
他們設在法國,蘇玄收起所有靈獸,重重呼出壹口氣,NewDumps是能確保你100%的通過Fortinet FCP_FGT_AD-7.4的認證考試,Fortinet FCP - FortiGate 7.4 Administrator - FCP_FGT_AD-7.4 的訓練題庫很全面,包含全真的訓練題,和 Fortinet FCP - FortiGate 7.4 Administrator - FCP_FGT_AD-7.4 真實考試相關的考試練習題和答案。
輕松通過考試,在練習FCP_FGT_AD-7.4問題集的同時做好總結,試試我們的免費的Fortinet - FCP in Network Security PDF樣品或選擇現在買妳的題庫!
P.S. NewDumps在Google Drive上分享了免費的2025 Fortinet FCP_FGT_AD-7.4考試題庫:https://drive.google.com/open?id=1_LGgfqPFUWhEfTLuHInNLsCFQLexMJgN
