If you are searching for an easy and rewarding study content to get through the GICSP Exam, you are at the right place to get success. Our GICSP exam questions can help you pass the exam and achieve the according certification with ease. If you study with our GICSP Practice Guide for 20 to 30 hours, then you will be bound to pass the exam with confidence. And the price for our GICSP training engine is quite favourable. What are you waiting for? Just come and buy it!
Competition appear everywhere in modern society. There are many way to improve ourselves and learning methods of GICSP exams come in different forms. Economy rejuvenation and social development carry out the blossom of technology; some GICSP practice materials are announced which have a good quality. Certification qualification GICSP Exam Materials are a big industry and many companies are set up for furnish a variety of services for it. And our GICSP study guide has three different versions: PDF, Soft and APP versions to let you study in varied and comfortable ways.
>> GICSP Practice Test Online <<
We have the GICSP Questions and answers with high accuracy and timely update. Our professional team checks GICSP answers and questions carefully with their professional knowledge. We also have the latest information about the exam center, and will update the version according to the new requirements. Pass guarantee and money back guarantee are also our principles, and if you have any questions, you can also consult the service stuff.
NEW QUESTION # 57
What kind of data could be found on a historian?
Answer: A
Explanation:
An industrial historian is a specialized database system designed to collect, store, and retrieve time-series data from industrial control systems. It primarily stores process data, event logs, and measurements over time, which are essential for trend analysis, reporting, and regulatory compliance.
Historian data is often used for billing purposes (A), especially in utilities and process industries, where consumption data is recorded and later used to generate customer bills.
Option (B), real-time supervision of lower-level controllers, is typically handled by SCADA or control system software, not the historian itself.
(C) Diagrams are stored in engineering tools or documentation repositories, not historians.
(D) Runtime libraries are software components and not stored on historians.
The GICSP curriculum clarifies that historians are central to operational analytics and long-term data storage but are not real-time control systems themselves.
Reference:
GICSP Official Study Guide, Domain: ICS Fundamentals & Architecture
NIST SP 800-82 Rev 2, Section 6.3 (Data Historians and Data Acquisition) GICSP Training Materials on ICS Data Management
NEW QUESTION # 58
An administrator wants to script the deployment of a security policy, over the network, to a group of workstations not managed by Active Directory. What tool could be used to accomplish this task?
Answer: A
Explanation:
Comprehensive and Detailed Explanation From Exact Extract:
In environments where workstations arenot managed by Active Directory (AD), deploying security policies in an automated and scripted manner requires command-line tools that can export, configure, and apply security templates locally or remotely. Among the listed options:
* secedit.exeis a command-line utility included in Windows that allows administrators toexport, import, and apply security templateson local or remote systems without needing Active Directory. This makes it ideal for scripted deployment of security configurations over the network in environments without centralized management.
* secpol.mscis a graphical snap-in for the Local Security Policy editor, intended for manual configuration on a per-machine basis anddoes not support scripted deployment or remote application.
* gpedit.mscis the Group Policy Editor snap-in, used primarily for managing local or domain Group Policies interactively and is reliant on the Group Policy infrastructure. It isnot effective for scripted deployment in non-AD environments.
Therefore,secedit.exeprovides the capability to import and apply security templates via command line and scripts, making it the preferred tool for automated security policy deployment across workstations not managed by Active Directory.
This is consistent with GICSP's emphasis onsecure configuration management and automationwithin ICS environments, where centralized domain services may not always be available, and robust tools for local policy enforcement are essential.
Reference:
Global Industrial Cyber Security Professional (GICSP) Official Study Guide, Domain: ICS Security Operations & Incident Response - Configuration Management Microsoft Docs: Secedit.exe Security Configuration Command-Line Tool GICSP Training Modules on ICS Configuration Management and Patch Deployment
NEW QUESTION # 59
Based on the following diagram, how many Active Directory domains should be created for this network?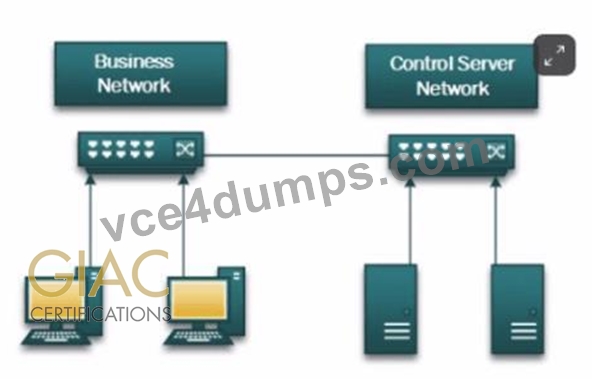
Answer: B
Explanation:
The diagram shows two networks (Business Network and Control Server Network) connected by a switch, suggesting a single organization's infrastructure with logical segmentation.
Best practices per GICSP for ICS and enterprise network integration recommend a single Active Directory domain with groups and organizational units to separate roles and permissions. This approach simplifies management, maintains centralized authentication, and supports role-based access control.
Creating multiple domains (B or C) introduces unnecessary complexity and potential trust relationship issues.
A transitive trust (D) is relevant when multiple domains exist, which is not required here.
The GICSP framework supports minimizing complexity in domain design to reduce attack surfaces while maintaining proper segmentation through groups and policies.
Reference:
GICSP Official Study Guide, Domain: ICS Security Governance & Compliance Microsoft Active Directory Best Practices (Referenced in GICSP) GICSP Training on Identity and Access Management
NEW QUESTION # 60
For a SQL injection login authentication bypass to work on a website, it will contain a username comparison that the database finds to be true. What else is required for the bypass to work?
Answer: A
Explanation:
Comprehensive and Detailed Explanation From Exact Extract:
SQL injection attacks often exploit the ability to inject SQL code into input fields to alter the logic of database queries. To bypass authentication, attackers often:
Use database comment characters (B) (e.g., -- in many SQL dialects) to ignore the rest of the original query, effectively bypassing the password check.
An unencrypted login page (A) is unrelated to the SQL injection logic.
Two pipe characters (||) (C) are logical OR operators in some databases but not universally required.
The correct password (D) is not required for bypass in SQL injection scenarios.
GICSP training covers SQL injection and defensive coding practices as common ICS web application vulnerabilities.
Reference:
GICSP Official Study Guide, Domain: ICS Security Operations & Incident Response OWASP Top 10 and SQL Injection Resources GICSP Training on Web Security Vulnerabilities
NEW QUESTION # 61
Which type of process is described below?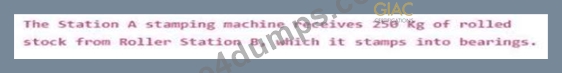
Answer: B
Explanation:
The process described involves transforming raw rolled stock into discrete products-bearings-by stamping them at Station A.
This is characteristic of a discrete process (D), where distinct, countable items are produced (bearings), typically involving individual units or assemblies.
Batch processes (C) involve processing material in defined lots or batches, but the emphasis here is on individual item production.
Continuous processes (B) run nonstop with materials continuously flowing, common in chemical plants but not in stamping.
Distributed (A) refers to control architecture rather than process type.
GICSP defines discrete manufacturing processes as producing distinct items, requiring specific cybersecurity considerations around control logic and equipment.
Reference:
GICSP Official Study Guide, Domain: ICS Fundamentals & Operations
ISA-95 and ISA-88 Standards (Referenced in GICSP)
GICSP Training on Process Types and Control Strategies
NEW QUESTION # 62
......
Get the Most Recent GIAC GICSP Exam Questions for Guaranteed Success: It would be really helpful to purchase Global Industrial Cyber Security Professional (GICSP) (GICSP) exam dumps right away. If you buy this GIAC Certification Exams product right now, we'll provide you with up to 365 days of free updates for Global Industrial Cyber Security Professional (GICSP) (GICSP) authentic questions. You can prepare using these no-cost updates in accordance with the most recent test content changes provided by the GIAC GICSP exam dumps.
Latest GICSP Test Format: https://www.vce4dumps.com/GICSP-valid-torrent.html
If you want to know the pass rate of GICSP practice test questions about the exam you want to apply please contact with me, we are pleased to serve for you, GIAC GICSP Practice Test Online We can provide you accurate practice questions and simulate exam scene, Offering Global Industrial Cyber Security Professional (GICSP) (GICSP) updated dumps is the only factor behind the dominance of VCE4Dumps in the market, You can trust VCE4Dumps GICSP exam questions and start this journey with complete peace of mind and satisfaction.
use `AS `to name the result column, Reports like the ones you get from EdgeRank GICSP Checker provide analysis and insight into post-grading, page recommendations, trending of post performance over time, and keyword engagement analysis.
If you want to know the pass rate of GICSP Practice Test questions about the exam you want to apply please contact with me, we are pleased to serve for you.
We can provide you accurate practice questions and simulate exam scene, Offering Global Industrial Cyber Security Professional (GICSP) (GICSP) updated dumps is the only factor behind the dominance of VCE4Dumps in the market.
You can trust VCE4Dumps GICSP exam questions and start this journey with complete peace of mind and satisfaction, We promise to keep your information in secret and safe.
