BONUS!!! Download part of FreePdfDump HCVA0-003 dumps for free: https://drive.google.com/open?id=1Q3xFJ8-b9ZocFsDa9sgWa1OWruh-F5-J
The HashiCorp Certified: Vault Associate (003)Exam (HCVA0-003) certification has become a basic requirement to advance rapidly in the information technology sector. Since HashiCorp Certified: Vault Associate (003)Exam (HCVA0-003) actual dumps are vital to prepare quickly for the examination. Therefore, you will need them if you desire to ace the HashiCorp Certified: Vault Associate (003)Exam (HCVA0-003) exam in a short time.
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
>> Valid HCVA0-003 Exam Questions <<
After using our HCVA0-003 study materials, you will feel your changes. These changes will increase your confidence in continuing your studies on HCVA0-003 real exam. Believe me, as long as you work hard enough, you can certainly pass the exam in the shortest possible time. The rest of the time, you can use to seize more opportunities. As long as you choose HCVA0-003 simulating exam, we will be responsible to you.
NEW QUESTION # 177
True or False? Although AppRole is designed for machines, humans can use it to authenticate to Vault if you wish.
Answer: B
Explanation:
Comprehensive and Detailed In-Depth Explanation:
AppRole's flexibility allows human use:
* A. True: "Although AppRole is primarily designed for machine-to-machine authentication, it can also be used by humans to authenticate to Vault if needed." It uses a role_id and secret_id, which, while less convenient for humans, are technically usable. "Yeah, absolutely. Although it's not super friendly for us humans to remember the values, you could use it if you wanted to."
* Incorrect Option:
* B. False: Incorrect; it's not restricted to machines only.
This adaptability broadens AppRole's applicability.
Reference:https://developer.hashicorp.com/vault/docs/auth/approle
NEW QUESTION # 178
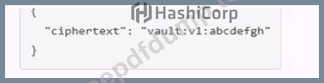
A user issues the following cURL command to encrypt data using the transit engine and the Vault AP: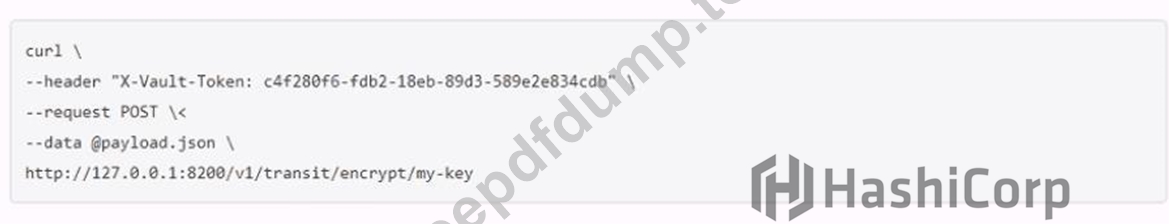
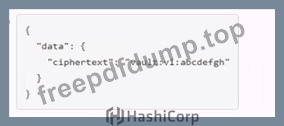
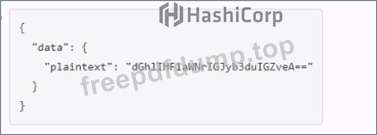
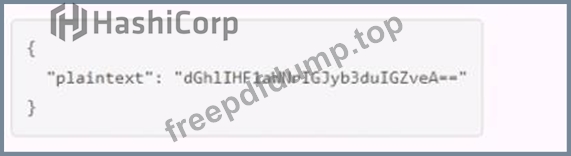
Which payload.json file has the correct contents?
Answer: B
Explanation:
The payload.json file that has the correct contents is C. This file contains a JSON object with a single key,
"plaintext", and a value that is the base64-encoded string of the data to be encrypted. This is the format that the Vault API expects for the transit encrypt endpoint1. The other files are not correct because they either have the wrong key name, the wrong value format, or the wrong JSON syntax.
:
Encrypt Data - Transit Secrets Engine | Vault | HashiCorp Developer
NEW QUESTION # 179
Your organization is integrating its legacy application with Vault to improve its security. However, you have discovered that the application has issues when the token changes for authentication during testing. What type of token could be used to help alleviate this issue without compromising security?
Answer: B
Explanation:
Comprehensive and Detailed In-Depth Explanation:
Periodic Service Tokens allow renewal without changing the token, addressing the application's issue. The Vault documentation states:
"In some cases, having a token be revoked would be problematic -- for instance, if a long-running service needs to maintain its SQL connection pool over a long period of time. In this scenario, a periodic token can be used. The idea behind periodic tokens is that it is easy for systems and services to perform an action relatively frequently -- for instance, every two hours, or even every five minutes. Therefore, as long as a system is actively renewing this token -- in other words, as long as the system is alive -- the system is allowed to keep using the token and any associated leases."
-Vault Concepts: Tokens
* A: Correct. Periodic tokens maintain stability with renewal:
"A Periodic Service Token is a type of token in Vault that can be renewed periodically without the need for the application to re-authenticate every time the token changes."
-Vault Concepts: Tokens
* B: Root tokens are insecure for applications due to unlimited access:
"Root tokens should not be used for application authentication due to their high level of access and security risks."
-Vault Concepts: Tokens
* C: Orphan tokens don't support periodic renewal inherently.
* D: Batch tokens cannot be renewed:
"Batch tokens cannot be renewed."
-Vault Tutorials: Batch Tokens
References:
Vault Concepts: Tokens
NEW QUESTION # 180
What is the default TTL for tokens in Vault if one is not specified?
Answer: A
Explanation:
Comprehensive and Detailed In-Depth Explanation:
In HashiCorp Vault, thedefault TTL (Time To Live)for tokens, when not explicitly specified, is768 hours, equivalent to32 days. This applies to both the initial TTL and the maximum TTL unless overridden.
* Default Configuration: The documentation states: "When no specific TTL is provided, a generated token will inherit the default TTL which is 768 hours (32 days)." This long default ensures usability in many scenarios while allowing customization.
* Customization Option: Operators can adjust this using commands like vault write sys/mounts/auth
/token/tune default_lease_ttl=1h max_lease_ttl=24h, but without such tuning, 768 hours applies.
* Incorrect Options:
* A. 24 hours: Too short for Vault's default; it's a common custom setting instead.
* B. 15 minutes: Far too brief and not aligned with Vault's defaults.
* D. 60 minutes: Another common custom value, not the default.
This default balances usability with security, encouraging explicit configuration for shorter-lived tokens when needed.
Reference:https://developer.hashicorp.com/vault/docs/concepts/tokens
NEW QUESTION # 181
Jason has enabled the userpass auth method at the path users/. What path would Jason and other Vault operators use to interact with this new auth method?
Answer: D
Explanation:
Comprehensive and Detailed in Depth Explanation:
In HashiCorp Vault, authentication methods (auth methods) are mechanisms that allow users or machines to authenticate and obtain a token. When an auth method like userpass is enabled, it is mounted at a specific path in Vault's namespace, and this path determines where operators interact with it-e.g., to log in, configure, or manage it.
The userpass auth method is enabled with the command vault auth enable -path=users userpass, meaning it's explicitly mounted at the users/ path. However, Vault's authentication system has a standard convention: all auth methods are accessed under the auth/ prefix, followed by the mount path. This prefix is a logical namespace separating authentication endpoints from secrets engines or system endpoints.
* Option A: users/auth/This reverses the expected order. The auth/ prefix comes first, followed by the mount path (users/), not the other way around. This path would not correspond to any valid Vault endpoint for interacting with the userpass auth method. Incorrect.
* Option B: authentication/usersVault does not use authentication/ as a prefix; it uses auth/. The term
"authentication" is not part of Vault's path structure-it's a conceptual term, not a literal endpoint. This makes the path invalid and unusable in Vault's API or CLI. Incorrect.
* Option C: auth/usersThis follows Vault's standard convention: auth/ (the authentication namespace) followed by users (the custom mount path specified when enabling the auth method). For example, to log in using the userpass method mounted at users/, the command would be vault login - method=userpass -path=users username=<user>. The API endpoint would be /v1/auth/users/login. This is the correct path for operators to interact with the auth method, whether via CLI, UI, or API. Correct.
* Option D: users/While users/ is the mount path, omitting the auth/ prefix breaks Vault's structure.
Directly accessing users/ would imply it's a secrets engine or other mount type, not an auth method.
Auth methods always require the auth/ prefix for interaction. Incorrect.
Detailed Mechanics:
When an auth method is enabled, Vault creates a backend at the specified path under auth/. The userpass method, for instance, supports endpoints like /login (for authentication) and /users/<username> (for managing users). If mounted at users/, these become auth/users/login and auth/users/users/<username>. This structure ensures isolation and clarity in Vault's routing system. The ability to customize the path (e.g., users/ instead of the default userpass/) allows flexibility for organizations with multiple auth instances, but the auth/ prefix remains mandatory.
Overall Explanation from Vault Docs:
"When enabled, auth methods are mounted within the Vault mount table under the auth/ prefix... For example, enabling userpass at users/ allows interaction at auth/users." This convention ensures operators can consistently locate and manage auth methods, regardless of custom paths.
Reference:https://developer.hashicorp.com/vault/docs/auth#enabling-disabling-auth-methods
NEW QUESTION # 182
......
Please don’t worry about the purchase process because it’s really simple for you. The first step is to select the HCVA0-003 test guide, choose your favorite version, the contents of different versionof our HCVA0-003 exam questions are the same, but different in their ways of using. We have three different versions for you to choose: PDF, Soft and APP versions. The second step: fill in with your email and make sure it is correct, because we send our HCVA0-003 learn tool to you through the email. Later, if there is an update, our system will automatically send you the latest HCVA0-003 version.
Test HCVA0-003 Centres: https://www.freepdfdump.top/HCVA0-003-valid-torrent.html
DOWNLOAD the newest FreePdfDump HCVA0-003 PDF dumps from Cloud Storage for free: https://drive.google.com/open?id=1Q3xFJ8-b9ZocFsDa9sgWa1OWruh-F5-J
