Key Features of FCP - FortiGate 7.4 Administrator Updated Practice Material! The FCP - FortiGate 7.4 Administrator practice material comes with multiple unique features. These features make your Fortinet Exam FCP - FortiGate 7.4 Administrator test preparation process simple and quick. The top listed features of FCP_FGT_AD-7.4 study material are actual test questions, free demo facility, three months of free FCP - FortiGate 7.4 Administrator test questions updates, affordable rate, and a full satisfaction guarantee. Our FCP - FortiGate 7.4 Administrator test preparation material comes in FCP_FGT_AD-7.4 PDF, FCP_FGT_AD-7.4 desktop practice test software, and web-based FCP_FGT_AD-7.4 practice exam.
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
>> Exam FCP_FGT_AD-7.4 Training <<
Fortinet PDF Questions can be used anywhere or at any time. You can download FCP_FGT_AD-7.4 dumps pdf files on your laptop, tablet, smartphone, or any other device. Practicing with Web-based and desktop FCP_FGT_AD-7.4 practice test software, you will get a strong grip on every Fortinet FCP_FGT_AD-7.4 exam topic. You can take multiple Fortinet FCP_FGT_AD-7.4 Practice Exam attempts and identify and overcome your mistakes. Furthermore, through Fortinet FCP_FGT_AD-7.4 practice test software you will improve your time-management skills. You will easily manage your time while attempting the actual FCP_FGT_AD-7.4 test.
NEW QUESTION # 54
Refer to the exhibit.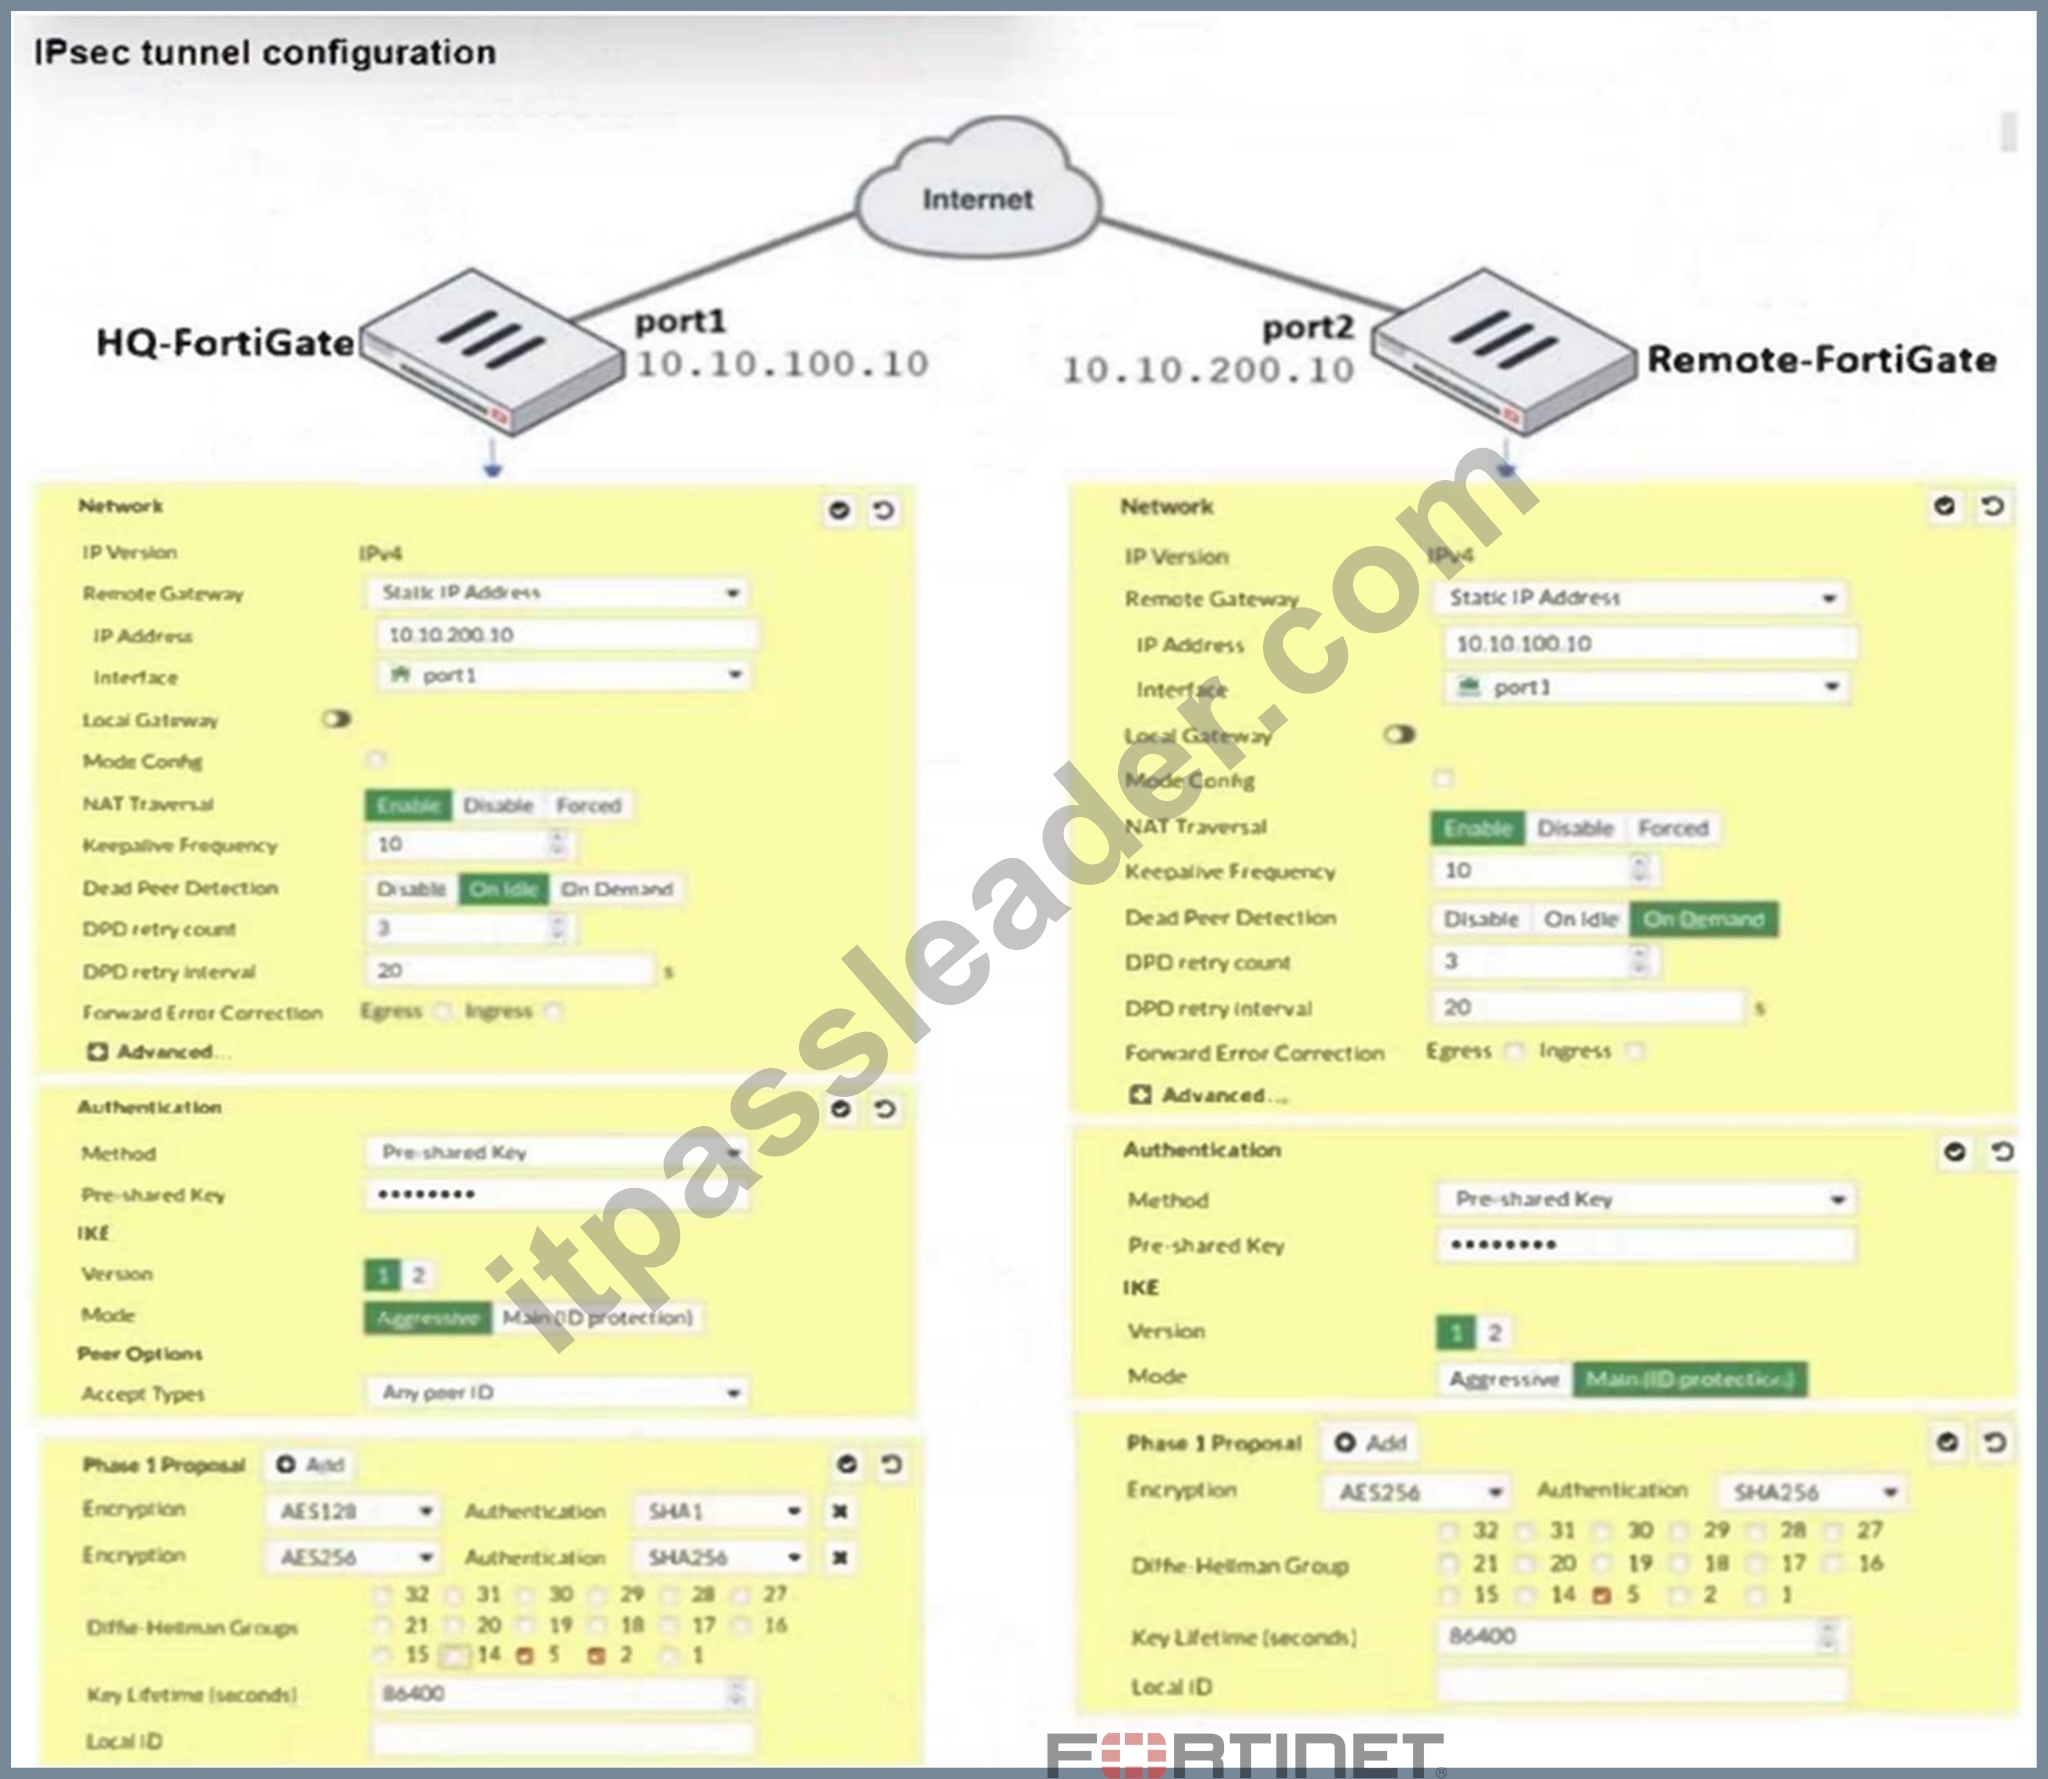
A network administrator is troubleshooting an IPsec tunnel between two FortiGate devices. The administrator has determined that phase 1 failed to come up. The administrator has also re-entered the pre-shared key on both FortiGate devices to make sure they match.
Based on the phase 1 configuration and the diagram shown in the exhibit, which two configuration changes can the administrator make to bring phase 1 up? (Choose two.)
Answer: B,D
Explanation:
To bring Phase 1 up, the following changes can be made:
A . On HQ-FortiGate, disable Diffie-Helman group 2: This is incorrect because Diffie-Hellman group 2 is already selected on both devices. Disabling it would not help.
B . On Remote-FortiGate, set port2 as Interface: This is incorrect as both sides should be consistent in their interface settings for the IPsec tunnel, and the interface is correctly set to port1 on both FortiGates in the IPsec configuration.
C . On both FortiGate devices, set Dead Peer Detection to On Demand: This is a valid option. Setting Dead Peer Detection (DPD) to "On Demand" helps maintain the IPsec connection by checking if the peer is still available, which can help in some cases where the connection fails due to timeouts.
D . On HQ-FortiGate, set IKE mode to Main (ID protection): This is also a valid option because the Remote-FortiGate is already set to Main mode (ID protection). Ensuring that both ends use the same mode is crucial for successful phase 1 negotiation.
Thus, the correct answers are:
C . On both FortiGate devices, set Dead Peer Detection to On Demand.
D . On HQ-FortiGate, set IKE mode to Main (ID protection).
NEW QUESTION # 55
Refer to the exhibit.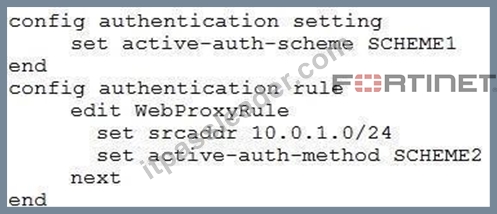
The exhibit shows a FortiGate configuration.
How does FortiGate handle web proxy traffic coming from the IP address 10.2.1.200, that requires authorization?
Answer: B
Explanation:
It authenticates the traffic using the authentication scheme SCHEME1.
What happens to traffic that requires authorization, but does not match any authentication rule? The active and passive SSO schemes to use for those cases is defined under config authentication setting.
NEW QUESTION # 56
Refer to the exhibits.
An administrator creates a new address object on the root FortiGate (Local-FortiGate) in the security fabric. After synchronization, this object is not available on the downstream FortiGate (ISFW).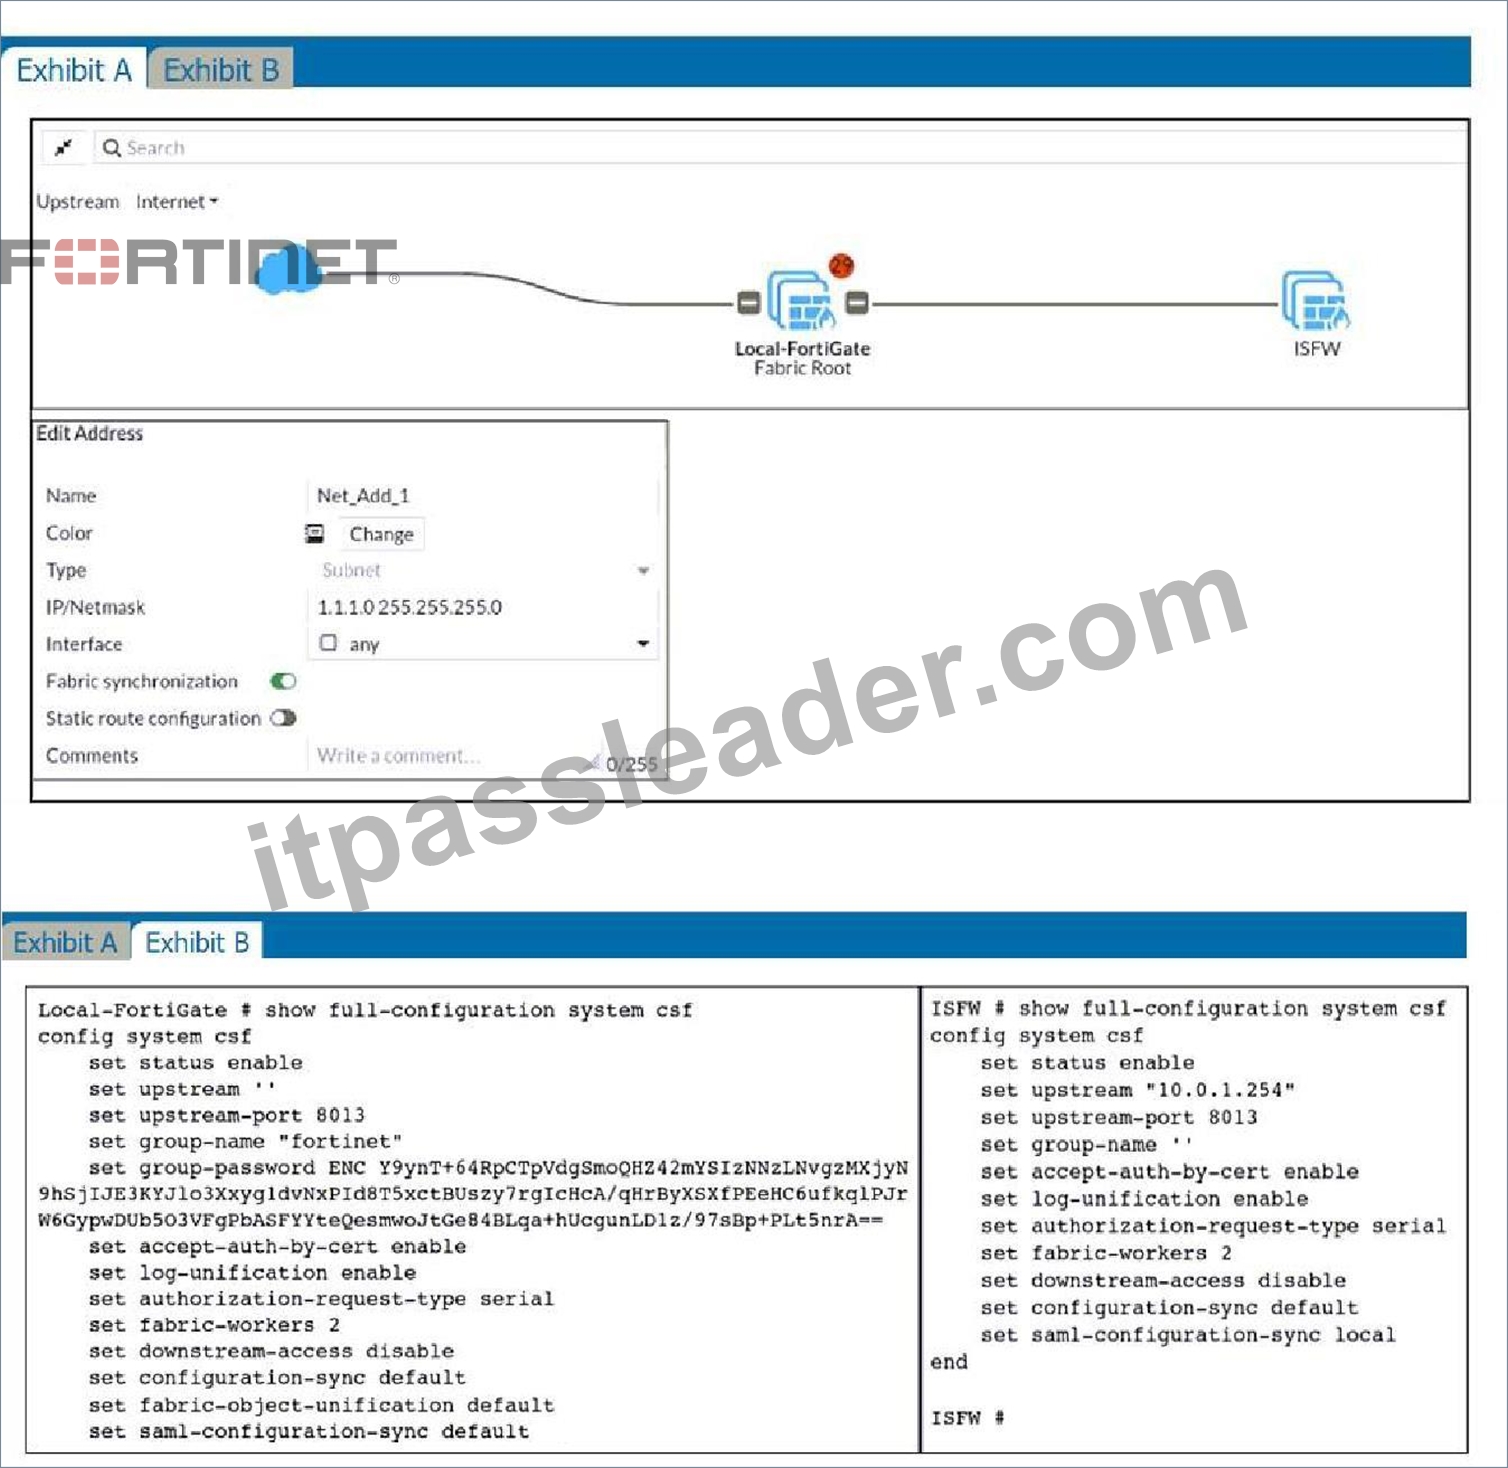
What must the administrator do to synchronize the address object?
Answer: B
Explanation:
C is correct because D is already set to default (Global CMDB objects will be synchronized in Security Fabric.) The root device has downstream access disabled, so it needs to be enabled to sync the object.
downstream-access - Enable/disable downstream device access to this device's configuration and data.
disable - Disable downstream device access to this device's configuration and data.
The CLI command "set fabric-object-unification" is only available on the root FortiGate.
NEW QUESTION # 57
Which method allows management access to the FortiGate CLI without network connectivity?
Answer: C
Explanation:
The serial console method allows management access to the FortiGate CLI without relying on network connectivity. This method involves directly connecting a computer to the FortiGate device using a serial cable (such as a DB-9 to RJ-45 cable or USB to RJ-45 cable) and using terminal emulation software to interact with the FortiGate CLI. This method is essential for situations where network-based access methods (such as SSH or Telnet) are not available or feasible.
References:
* FortiOS 7.4.1 Administration Guide: Console connection
NEW QUESTION # 58
To complete the final step of a Security Fabric configuration, an administrator must authorize all the devices on which device?
Answer: C
Explanation:
The correct answer is C. FortiAnalyzer.
Explanation:
In a Security Fabric configuration, after the devices are added to the Security Fabric, the final step is to authorize these devices. This authorization process is typically done through FortiAnalyzer, which manages and controls the Security Fabric. FortiAnalyzer allows administrators to centrally manage and monitor the Security Fabric, including authorizing devices to participate in the Security Fabric.
All devices must be authorized on the root Fortigate, and then after this step all must be authorized on the FortiAnalyzer.
NEW QUESTION # 59
......
The ITPassLeader is a reliable and trusted platform that is committed to making the FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) exam preparation instant, simple and successful. To do this the ITPassLeader is offering top-rated and real FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) exam questions with high-in-demand features. These features are inclusively designed to ace the Fortinet FCP_FGT_AD-7.4 exam preparation.
FCP_FGT_AD-7.4 Certification Dump: https://www.itpassleader.com/Fortinet/FCP_FGT_AD-7.4-dumps-pass-exam.html
