After cracking the FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) exam you will receive the credential badge. It will pave your way toward well-paying jobs or promotions in any reputed tech company. At TorrentVCE have customizable FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) practice exams for the students to review and improve their preparation. The FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) practice test material product of TorrentVCE are created by experts with the dedication to help customers crack the FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) exam on the first attempt.
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
>> Fortinet FCP_FGT_AD-7.4 Reliable Test Dumps <<
Our Fortinet FCP_FGT_AD-7.4 qualification test help improve your technical skills and more importantly, helping you build up confidence to fight for a bright future in tough working environment. Our professional experts devote plenty of time and energy to developing the FCP_FGT_AD-7.4 Study Tool. You can trust us and let us be your honest cooperator in your future development. Here are several advantages about our Fortinet FCP_FGT_AD-7.4 exam for your reference.
NEW QUESTION # 45
Refer to the exhibit.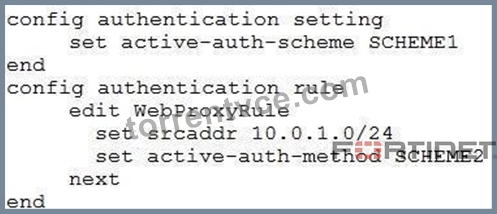
The exhibit shows a FortiGate configuration.
How does FortiGate handle web proxy traffic coming from the IP address 10.2.1.200, that requires authorization?
Answer: B
Explanation:
It authenticates the traffic using the authentication scheme SCHEME1.
What happens to traffic that requires authorization, but does not match any authentication rule? The active and passive SSO schemes to use for those cases is defined under config authentication setting.
NEW QUESTION # 46
An administrator configured a FortiGate to act as a collector for agentless polling mode.
What must the administrator add to the FortiGate device to retrieve AD user group information?
Answer: A
Explanation:
To retrieve AD user group information in agentless polling mode, the administrator must add an LDAP server to the FortiGate device.
NEW QUESTION # 47
Refer to the exhibits.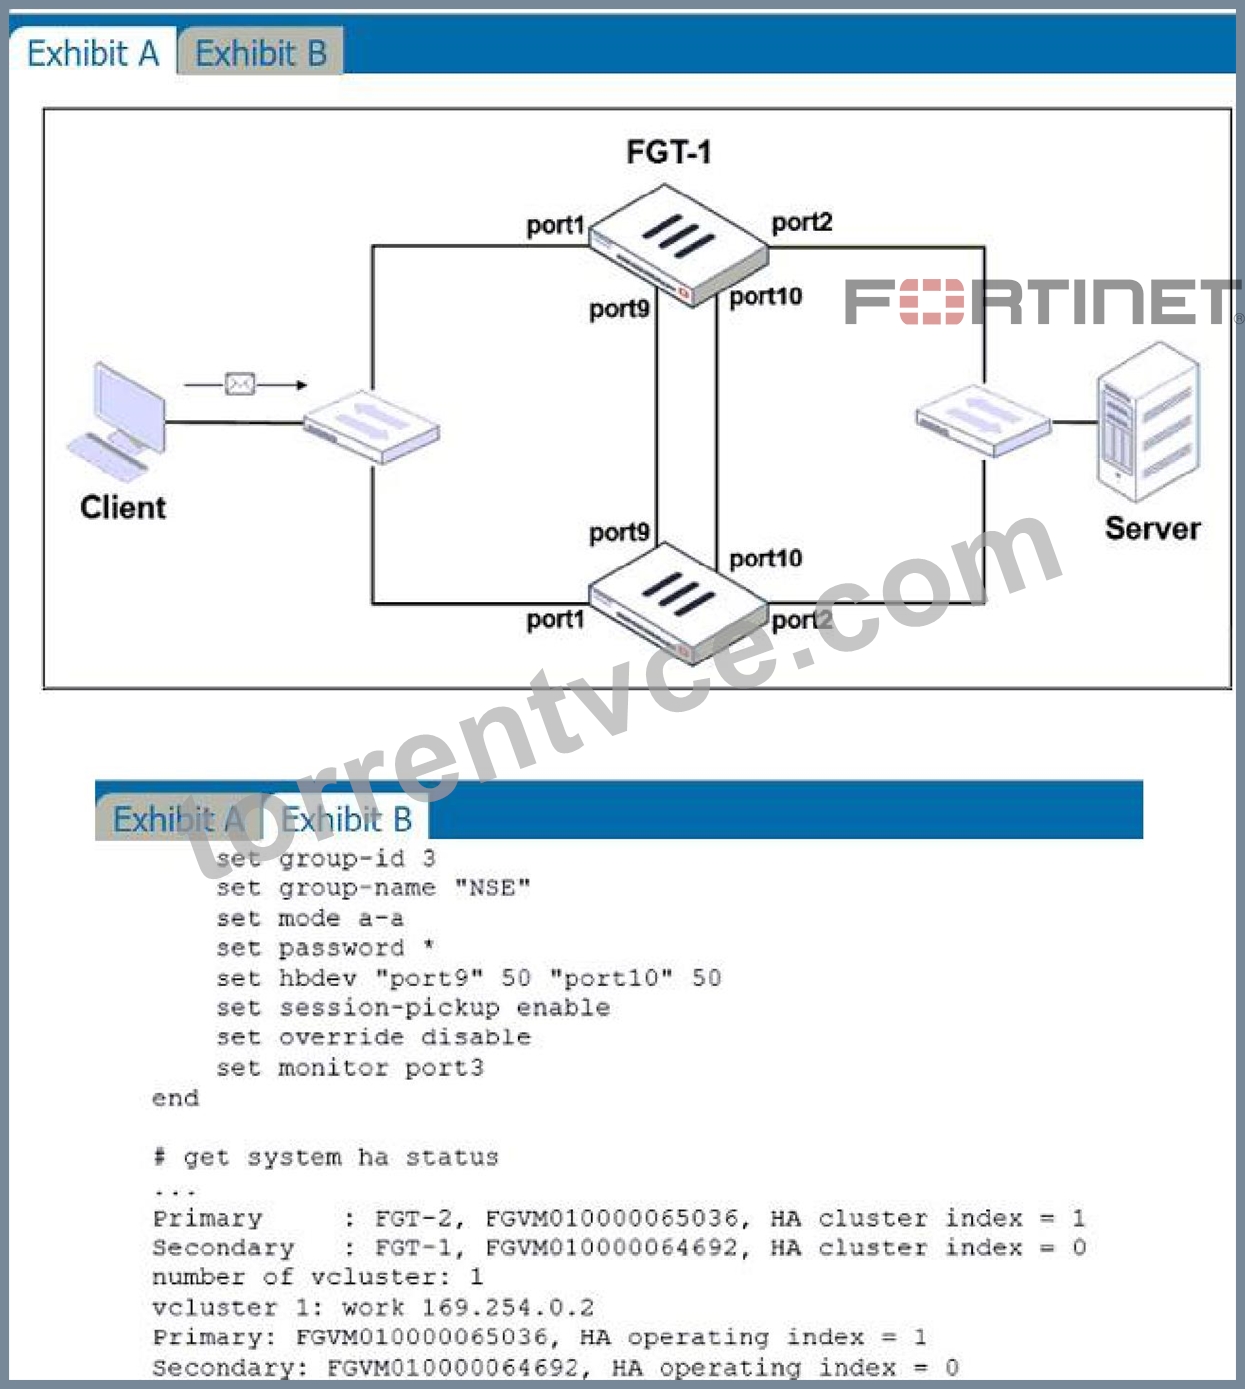
Exhibit A shows a topology for a FortiGate HA cluster that performs proxy-based inspection on traffic.
Exhibit B shows the HA configuration and the partial output of the get system ha status command.
Based on the exhibits, which two statements about the traffic passing through the cluster are true?
(Choose two.)
Answer: B,C
Explanation:
A: Non load balance: traffic enters port1 and go out port2 from FGT1. FGT2 is in primary mode D: In proxy inspection mode, SYN packet goes to FGT1 port1. It is then forwarded to FGT2. the source MAC address of the packet is changed to the physical MAC address of port1 on the primary and the destination MAC address to the physical MAC address of port1 on the secondary. This is also known as MAC address rewrite. In addition, the primary encapsulates the packet in an Ethernet frame type
0x8891. The encapsulation is done only for the first packet of a load balanced session
A. For non-load balanced connections, packets forwarded by the cluster to the server contain the virtual MAC address of port2 as source.
D. For load balanced connections, the primary encapsulates TCP SYN packets before forwarding them to the secondary.
Incorrect:
B. The traffic sourced from the client and destined to the server is sent to FGT-1. (not primary)
C. The cluster can load balance ICMP connections to the secondary. (not enabled) To forward traffic correctly, a FortiGate HA solution uses virtual MAC addresses.
The primary forwards the SYN packet to the selected secondary. (...) This is also known as MAC address rewrite. In addition, the primary encapsulates the packet in an Ethernet frame type 0x8891. The encapsulation is done only for the first packet of a load balanced session. The encapsulated packet includes the original packet plus session information that the secondary requires to process the traffic.
NEW QUESTION # 48
Which three options are the remote log storage options you can configure on FortiGate? (Choose three.)
Answer: A,C,E
Explanation:
B: FortiCloud
C: FortiSIEM
E: FortiAnalyzer
NEW QUESTION # 49
A network administrator has enabled full SSL inspection and web filtering on FortiGate. When visiting any HTTPS websites, the browser reports certificate warning errors. When visiting HTTP websites, the browser does not report errors.
What is the reason for the certificate warning errors?
Answer: C
Explanation:
When full SSL inspection is enabled, FortiGate intercepts HTTPS traffic, decrypts it for inspection, and re-encrypts it using its own SSL certificate before forwarding it to the browser. If the browser does not trust the SSL certificate being used by FortiGate for re-encryption, it will display certificate warning errors. To resolve this, the certificate used by FortiGate for SSL inspection must be installed and trusted in the browser's certificate store.
NEW QUESTION # 50
......
Whereas the other two FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) exam questions formats are concerned both are the easy-to-use and compatible mock FCP_FGT_AD-7.4 exam that will give you a real-time environment for quick Fortinet Exams preparation. Now choose the right FCP - FortiGate 7.4 Administrator (FCP_FGT_AD-7.4) exam questions format and start this career advancement journey.
Discount FCP_FGT_AD-7.4 Code: https://www.torrentvce.com/FCP_FGT_AD-7.4-valid-vce-collection.html
