BONUS!!! Download part of Exam-Killer SC-100 dumps for free: https://drive.google.com/open?id=1xcW41QrEUFroqWFywy9Kg0jj52fenfrS
The SC-100 study quiz is made from various experts for examination situation in recent years in the field of systematic analysis of finishing, meet the demand of the students as much as possible, at the same time have a professional staff to check and review SC-100 practice materials, made the learning of the students enjoy the information of high quality. Due to the variety of examinations, so that students can find the information on SC-100 guide engine they need quickly.
Our website experts simplify complex concepts of the SC-100 exam questions and add examples, simulations, and diagrams to explain anything that might be difficult to understand. Therefore, even ordinary examiners can master all the SC-100 learning materials without difficulty. And the price of our SC-100 Study Guide is reasonable for even the students can afford it. At the same time, we give some discounts from time to time, you can buy our SC-100 practice engine at a favorable price.
With our SC-100 exam materials, you will find that the difficult topics have been given special attention by our professional experts and explained with the help of examples, simulations and graphs. Our SC-100 study braindumps will certainly help candidates to enrich their knowledge in their daily work and be ready to answer all questions in the real exam. The benefits of studying our SC-100 learning guide is doubled to your expectation.
Microsoft SC-100 Certification Exam is a great opportunity for cybersecurity professionals to enhance their knowledge and skills in the field of cybersecurity architecture. SC-100 exam covers a wide range of topics, including security principles, identity and access management, threat protection, data protection, and application security. It is an excellent certification for those who wish to specialize in cybersecurity architecture and want to develop their career in this field.
NEW QUESTION # 56
You are designing a security strategy for providing access to Azure App Service web apps through an Azure Front Door instance.
You need to recommend a solution to ensure that the web apps only allow access through the Front Door instance.
Solution: You recommend configuring gateway-required virtual network integration.
Does this meet the goal?
Answer: A
Explanation:
https://docs.microsoft.com/en-us/azure/app-service/app-service-ip-restrictions#restrict-access-to-a-specific-azure-front-door-instance
Topic 2, Fabrikam, Inc
Overview
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
* An Azure Active Directory (Azure AD) tenant named fabrikam.onmicrosoft.com that syncs with corp.fabnkam.com
* A single Azure subscription named Sub1
* A virtual network named Vnet1 in the East US Azure region
* A virtual network named Vnet2 in the West Europe Azure region
* An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAR enabled
* A Microsoft Sentinel workspace
* An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
* 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
* A resource group named TestRG that is used for testing purposes only
* An Azure Virtual Desktop host pool that contains personal assigned session hosts All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure-.
* An Azure AD tenant named contoso.onmicrosoft.com
* An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications. The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1.
The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
* Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
* Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
* Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation-. Machines should have a vulnerability assessment solution.
All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
* ClaimsApp will be deployed to Azure App Service instances that connect to Vnetl and Vnet2.
* Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
* ClaimsApp will access data in ClaimsDB.
* ClaimsDB must be accessible only from Azure virtual networks.
* The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
* Azure DevTest labs will be used by developers for testing.
* All the application code must be stored in GitHub Enterprise.
* Azure Pipelines will be used to manage application deployments.
* All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
* Internet-accessible applications must prevent connections that originate in North Korea.
* Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
* Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
* Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
* Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers;
* Every month, the membership of the ContosoDevelopers group must be verified.
* The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
* The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
NEW QUESTION # 57
Your company wants to optimize using Azure to protect its resources from ransomware.
You need to recommend which capabilities of Azure Backup and Azure Storage provide the strongest protection against ransomware attacks. The solution must follow Microsoft Security Best Practices.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.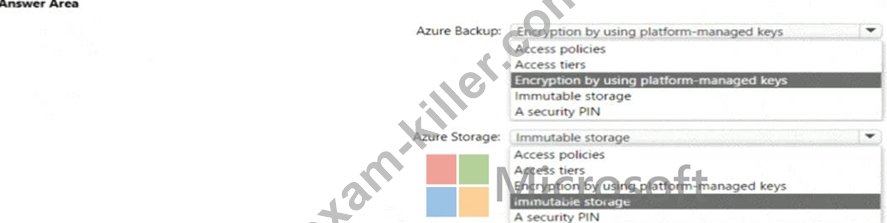
Answer:
Explanation: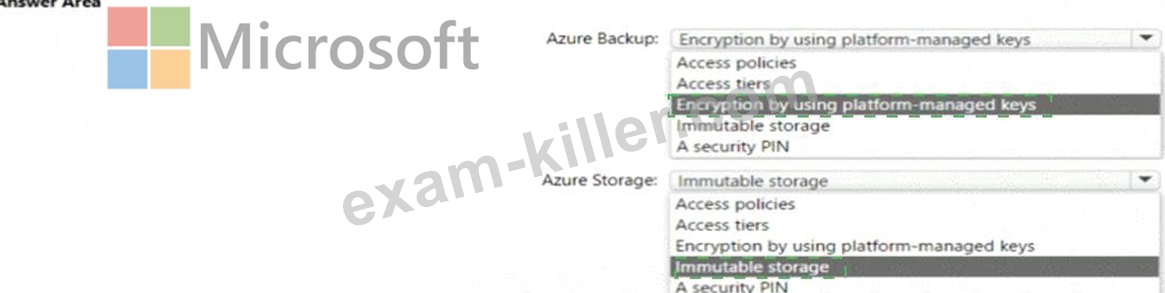
Explanation: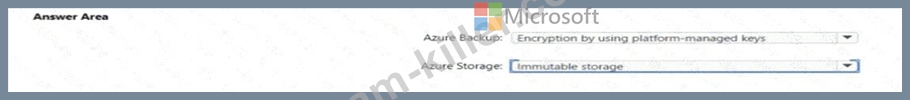
NEW QUESTION # 58
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.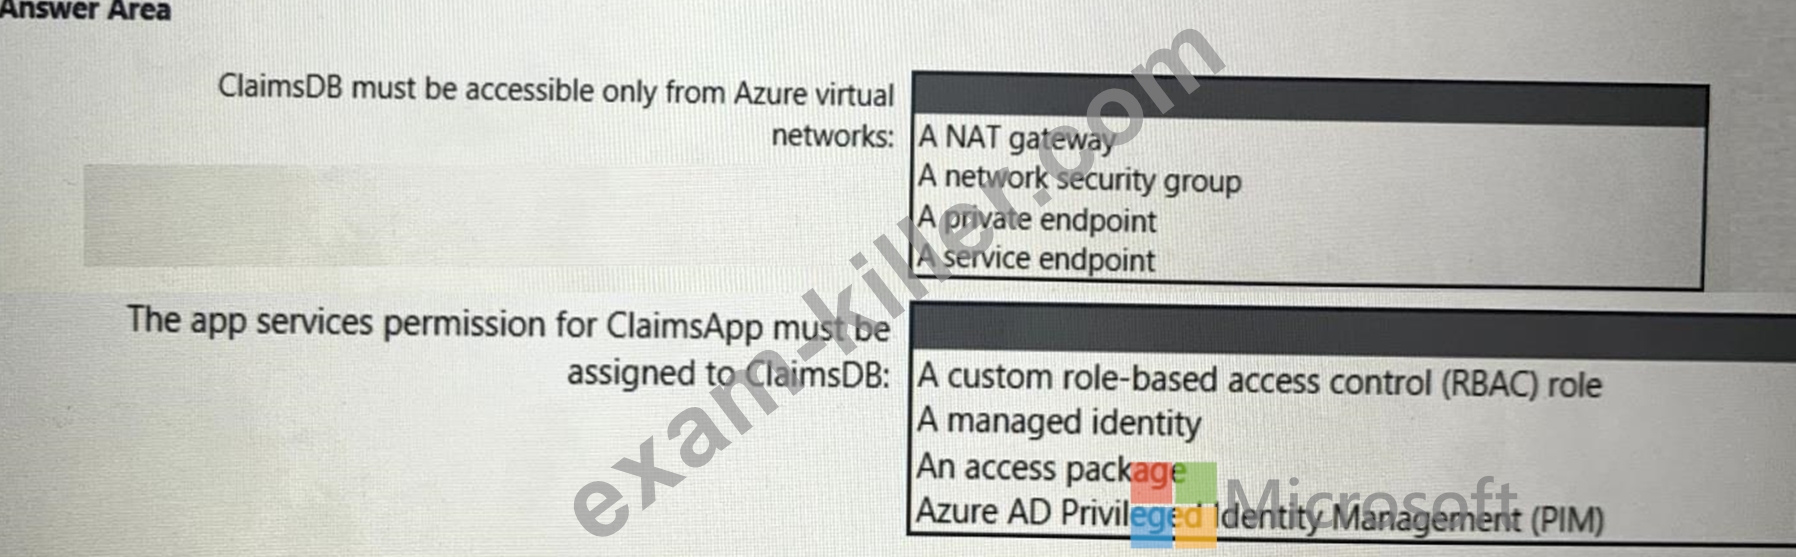
Answer:
Explanation: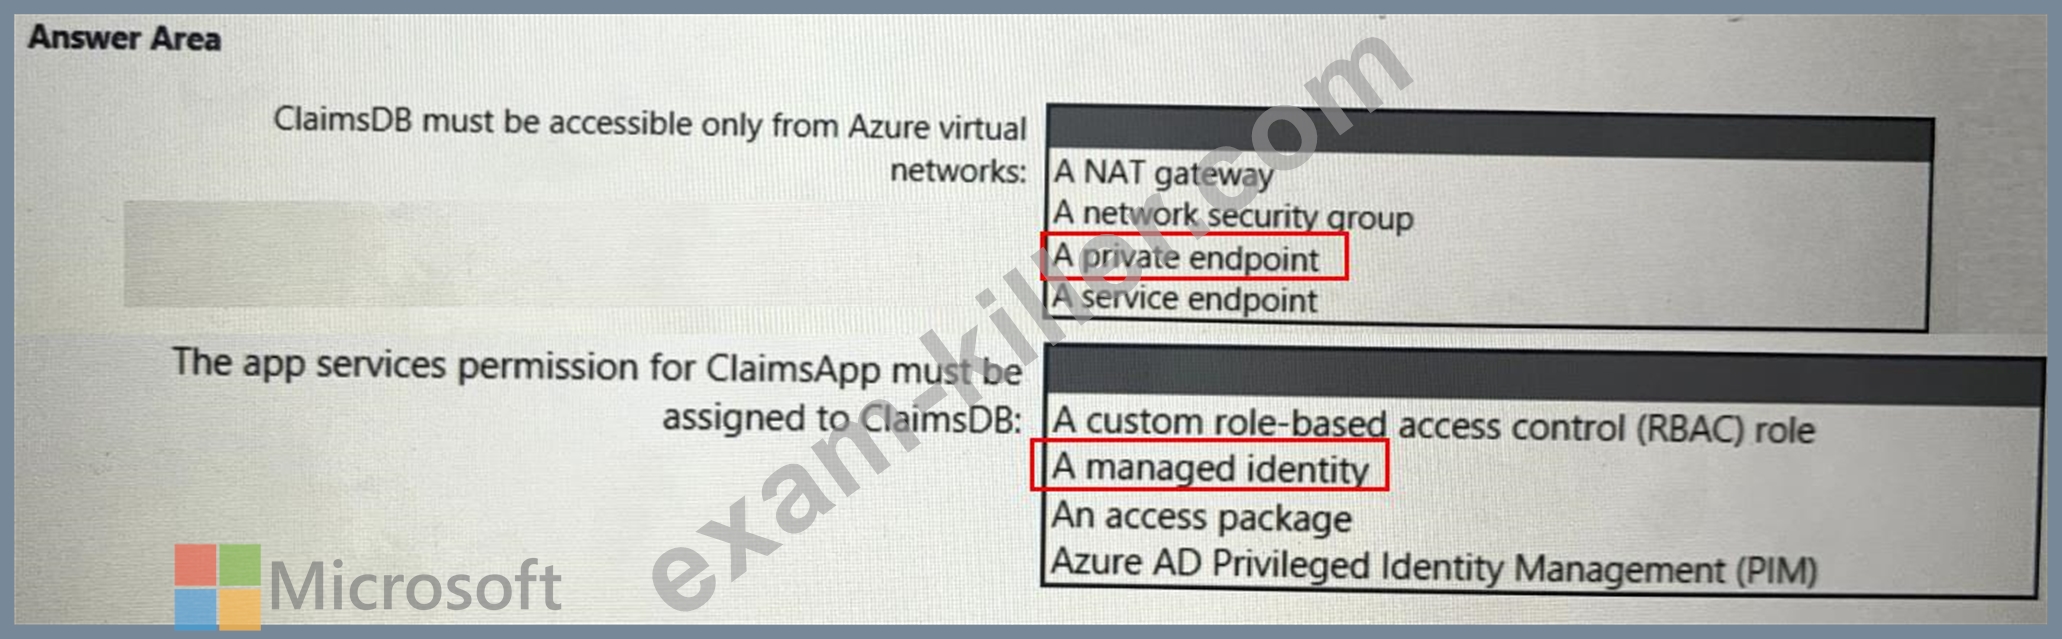
NEW QUESTION # 59
You have an Azure AD tenant that contains 10 Windows 11 devices and two groups named Group1 and Group2. The Windows 11 devices are joined to the Azure AD tenant and are managed by using Microsoft Intune.
You are designing a privileged access strategy based on the rapid modernization plan (RaMP). The strategy will include the following configurations:
* Each user in Group1 will be assigned a Windows 11 device that will be configured as a privileged access device.
* The Security Administrator role will be mapped to the privileged access security level.
* The users in Group1 will be assigned the Security Administrator role.
* The users in Group2 will manage the privileged access devices.
You need to configure the local Administrators group for each privileged access device. The solution must follow the principle of least privilege.
What should you include in the solution?
Answer: A
NEW QUESTION # 60
Your on-premises network contains an e-commerce web app that was developed in Angular and Nodejs. The web app uses a MongoDB database. You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.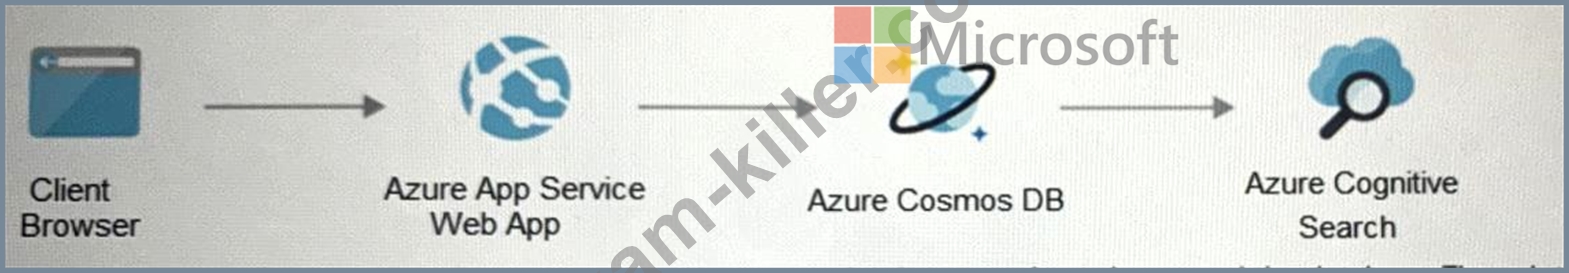
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model.
Solution: You recommend creating private endpoints for the web app and the database layer.
Does this meet the goal?
Answer: B
Explanation:
When using Azure-provided PaaS services (e.g., Azure Storage, Azure Cosmos DB, or Azure Web App, use the PrivateLink connectivity option to ensure all data exchanges are over the private IP space and the traffic never leaves the Microsoft network.
https://docs.microsoft.com/en-us/azure/cosmos-db/how-to-configure-private-endpoints
NEW QUESTION # 61
......
Our SC-100 learning materials are famous for high quality, and we have the experienced experts to compile and verify SC-100 exam dumps, the correctness and the quality can be guaranteed. SC-100 learning materials contain both questions and answers, and you can have a quickly check after you finish practicing. Moreover, we offer you free update for one year, and you can know the latest information about the SC-100 Exam Materials if you choose us. The update version will be sent to your email automatically.
SC-100 Reliable Dumps: https://www.exam-killer.com/SC-100-valid-questions.html
P.S. Free & New SC-100 dumps are available on Google Drive shared by Exam-Killer: https://drive.google.com/open?id=1xcW41QrEUFroqWFywy9Kg0jj52fenfrS
